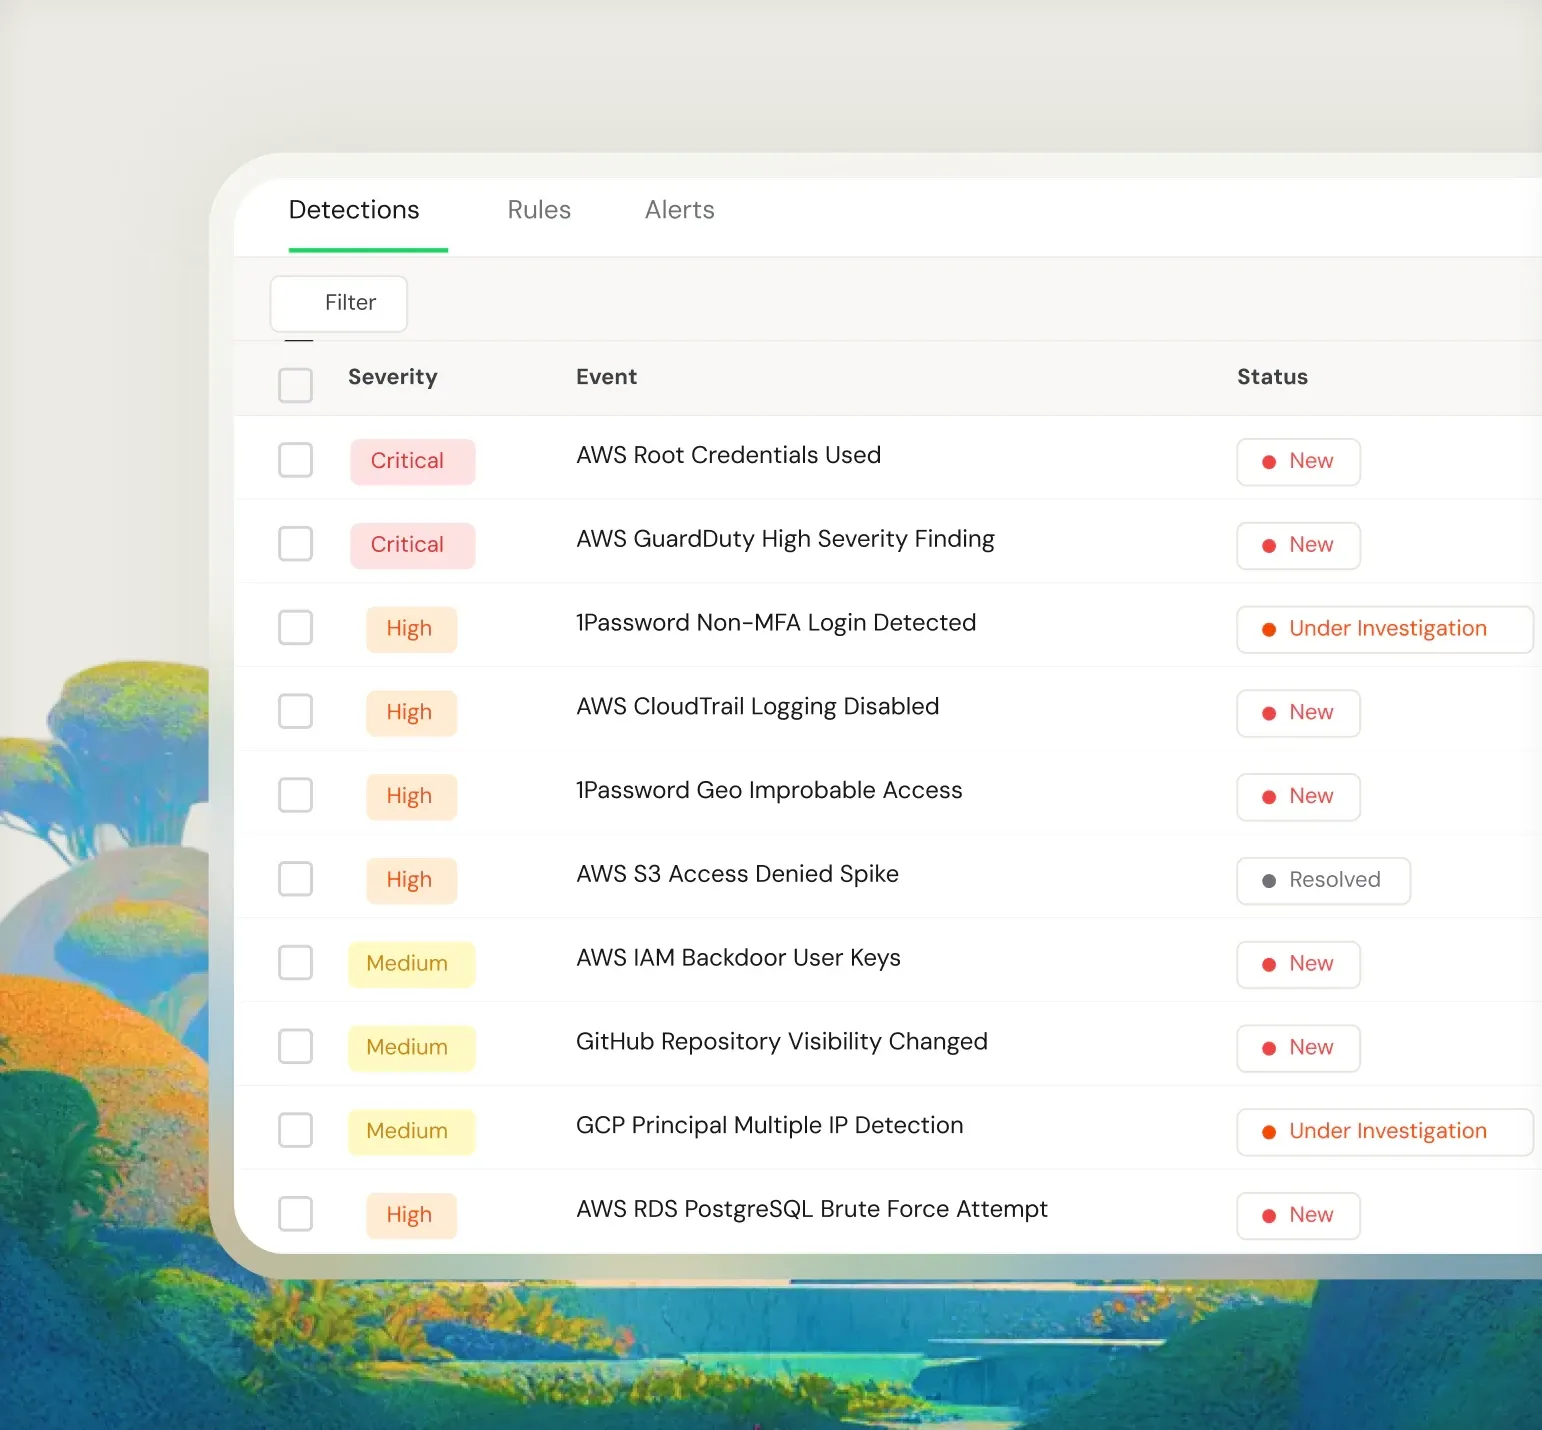
Security monitoring that works in minutes, not months
Real-time security monitoring with pre-built detection rules, configurable alerts, and a log explorer for threat hunting. Connect your cloud infrastructure and start detecting threats in minutes.
Why Fencer for Security Monitoring
Security monitoring built for startups
Connect your cloud infrastructure and start detecting threats immediately. No weeks of rule configuration or dedicated security team required.
Rules for AWS, GCP, 1Password, and GitHub are ready out of the box. Each includes remediation guidance so you know what to do when something fires.
Security monitoring is one part of a complete security foundation alongside vulnerability scanning, identity, code security, and more. One platform, one vendor, no tool sprawl.
Capabilities
Security monitoring features
See threats as they happen
Fencer continuously monitors your connected cloud services and flags security events as they happen. No manual log reviews required.
- Pre-built detection rules covering common cloud security threats
- Severity levels (Critical, High, Medium, Info) help you prioritize
- Status workflow to track investigation progress
- Assignable to team members for accountability
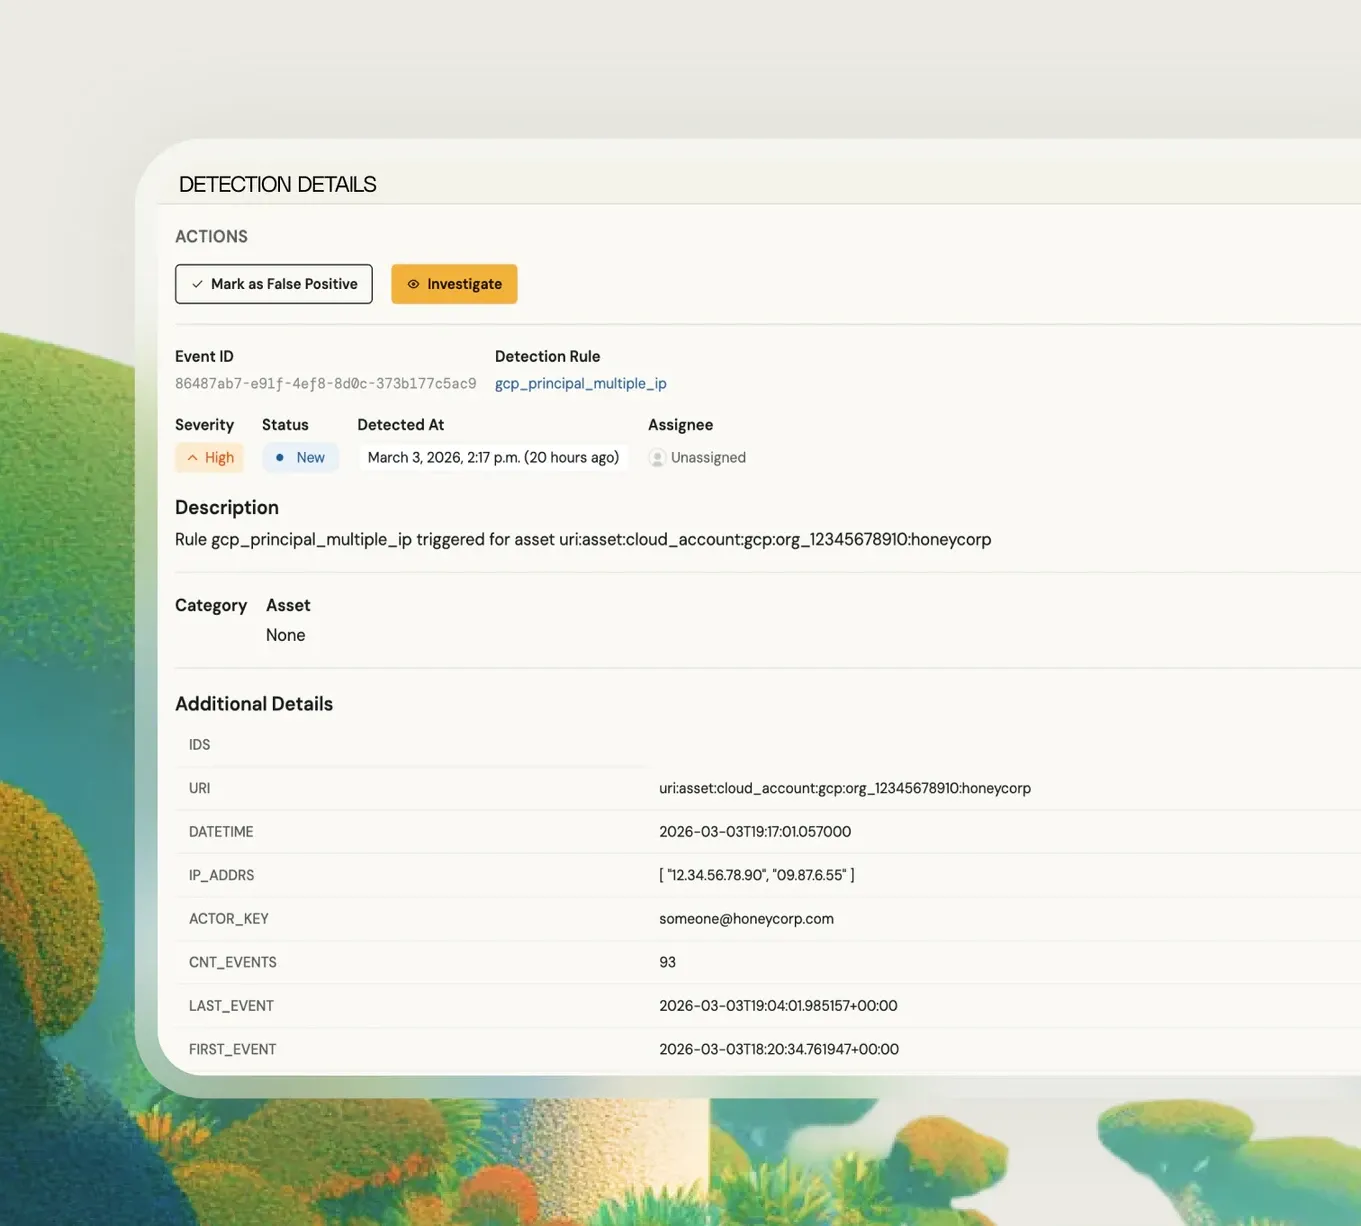
Detection rules with remediation guidance
Every detection rule comes with a description of what it catches, why it matters, and what to do about it. You don't need to be a security expert to respond appropriately.
- Event types include Access, Authentication, Intrusion, Network, and Malware
- Confidence scores indicate how likely an event is a real threat
- Remediation recommendations built into each rule
- Enable or disable rules based on your environment
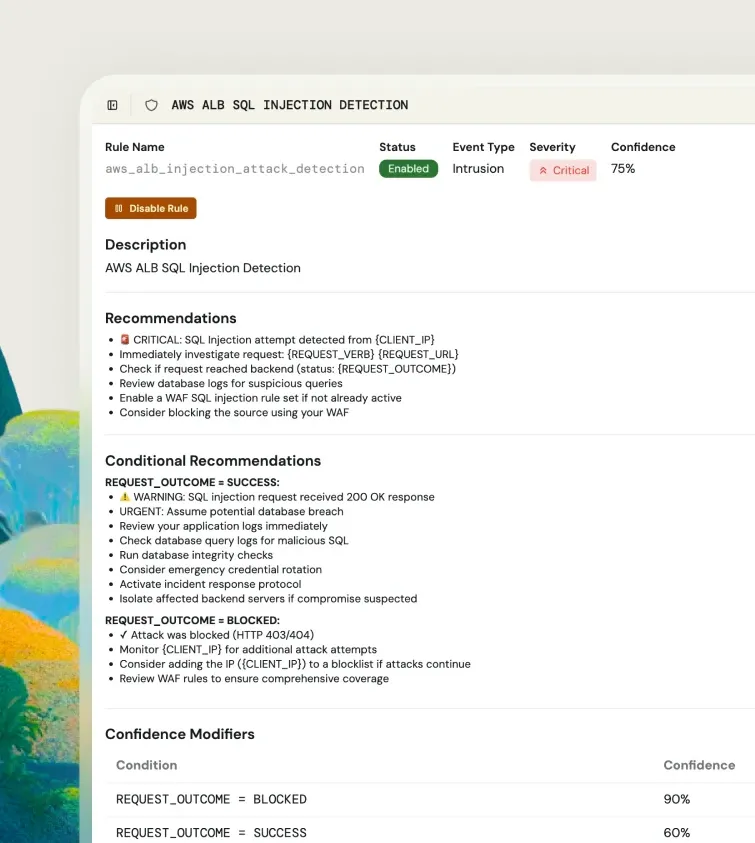
Get notified when it matters
Route alerts to the right people through the right channels. Set up multiple alert configurations for different scenarios, from real-time critical alerts to daily digests.
- Notification channels: Email, Slack, Webhook
- Filter by severity: Critical, High, Medium, Low
- Filter by event type: Intrusion, Network, Malware, Authentication, Access
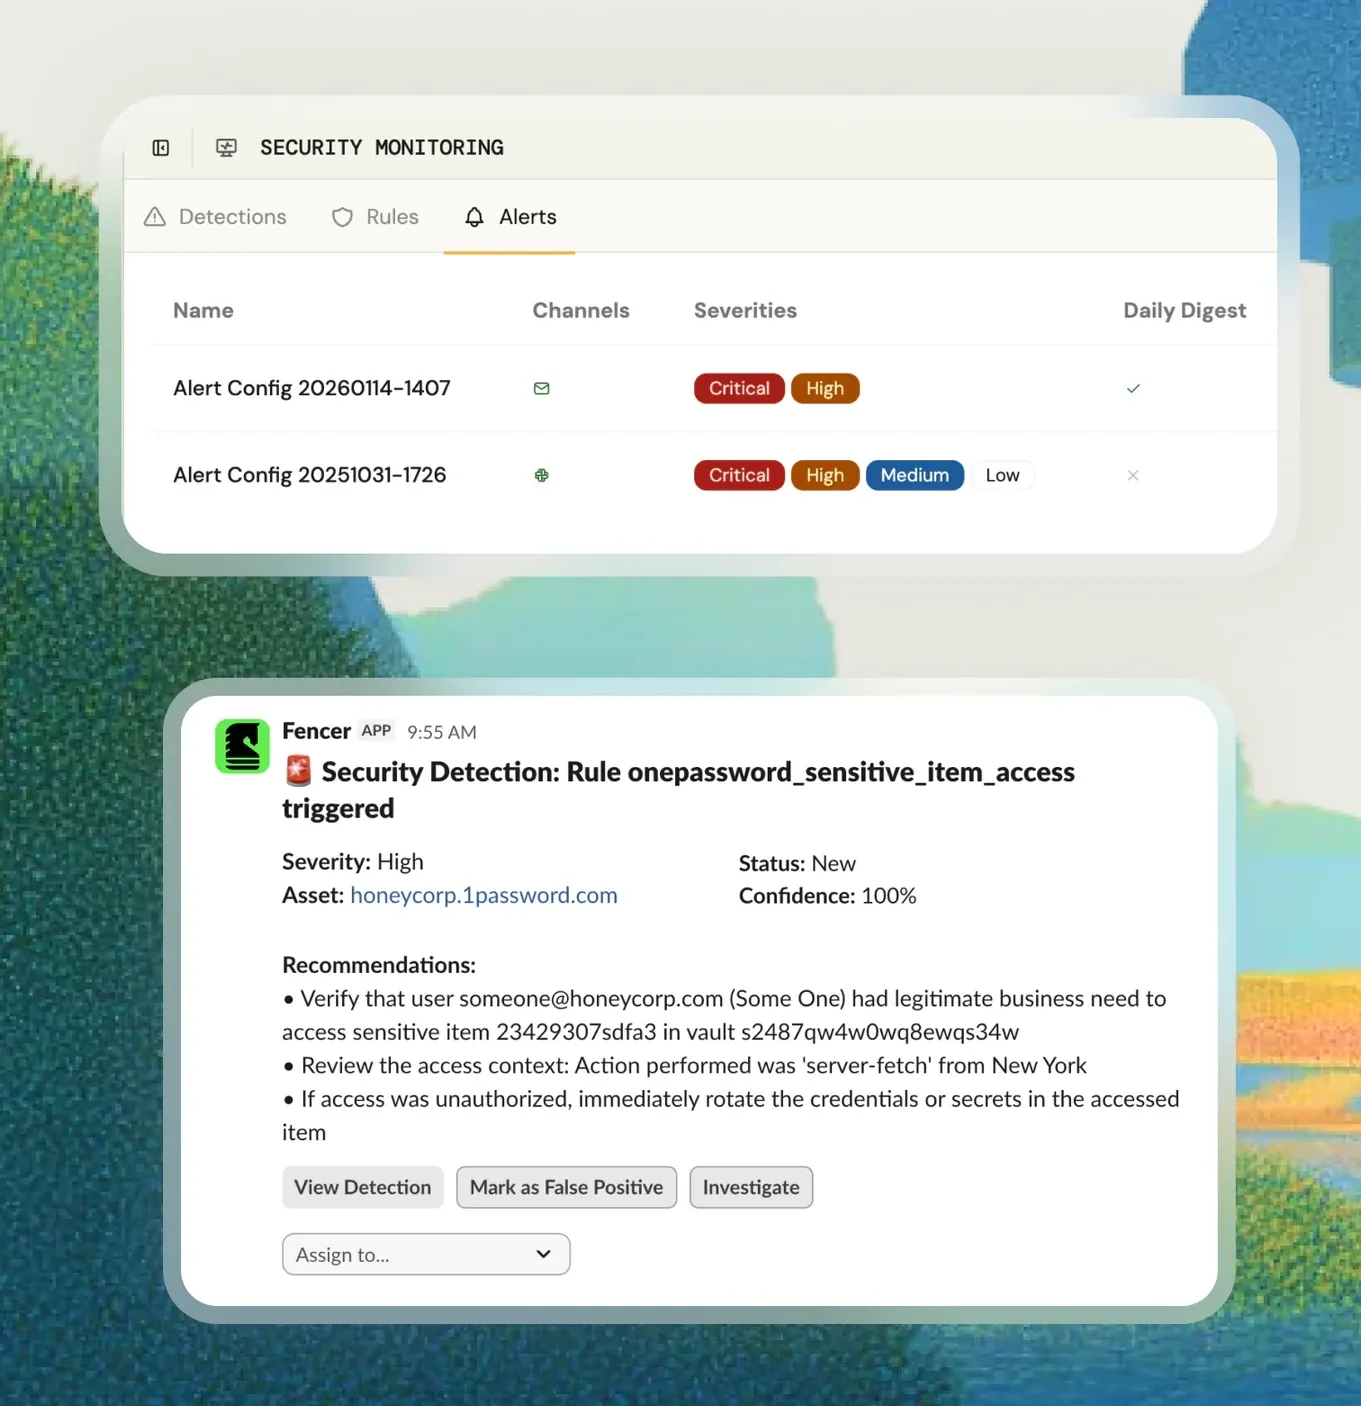
Explore your logs in real-time
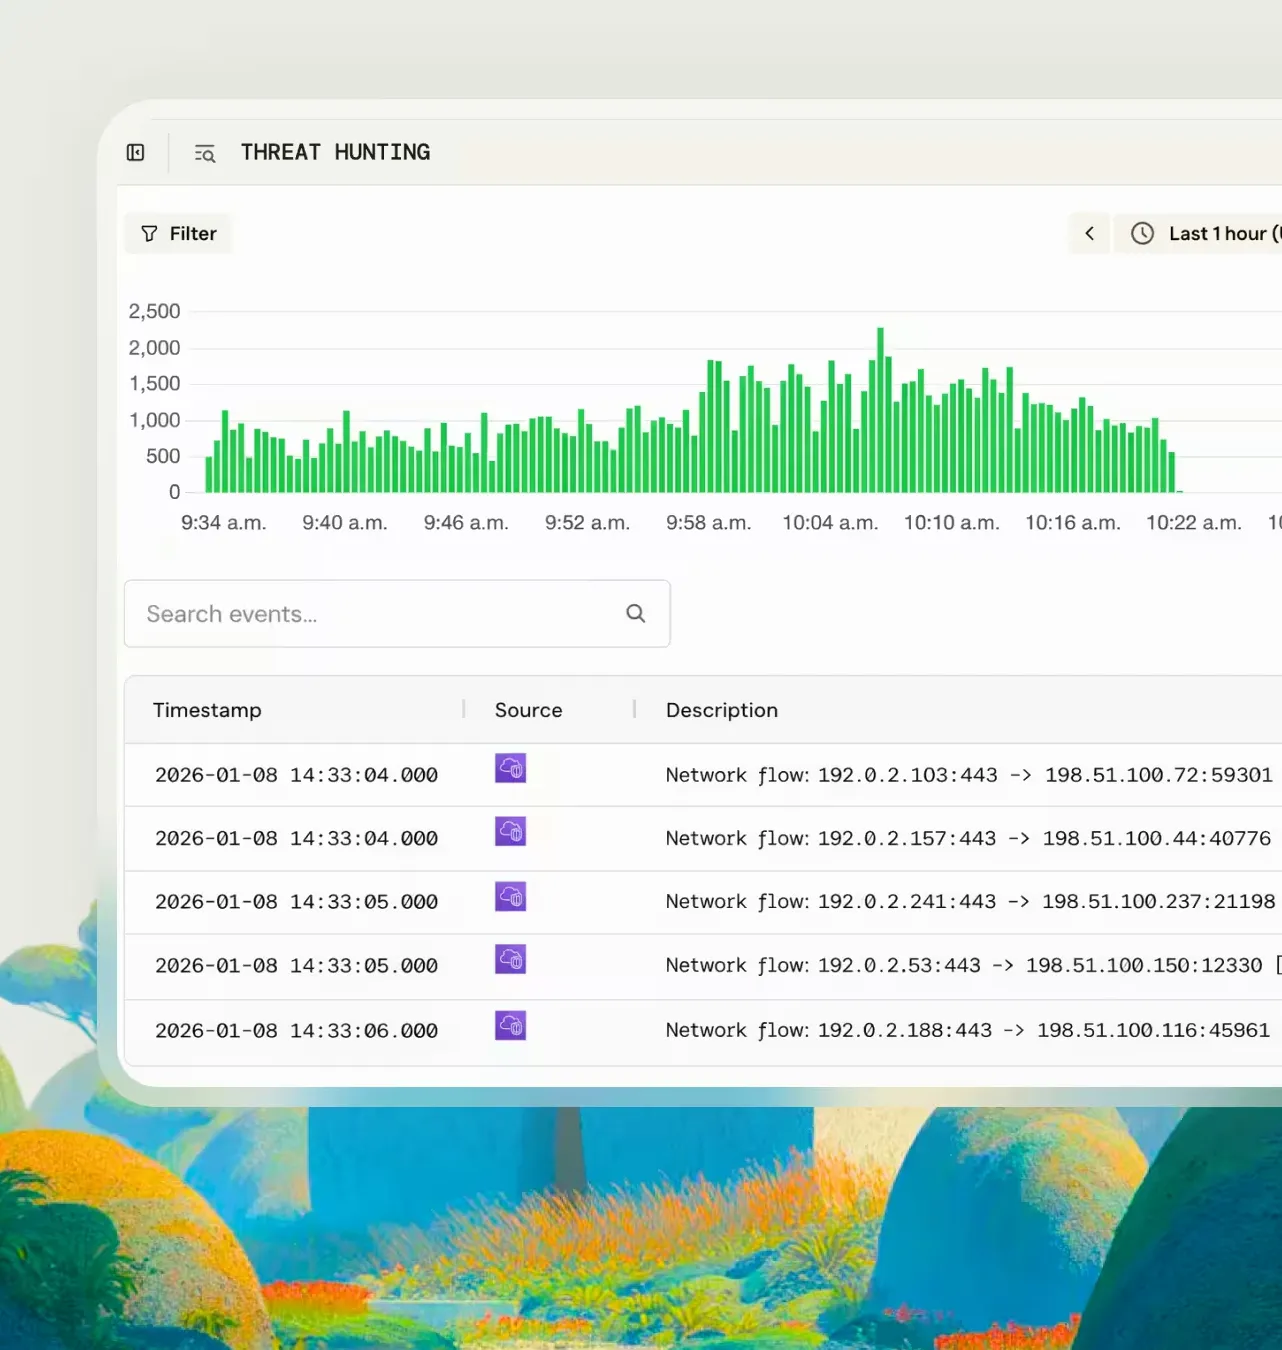
When you need to dig deeper, the threat hunting log explorer gives you full access to your security events. Search across all ingested logs, filter by source or message content, and export raw data for external analysis.
- Real-time event stream with volume histogram
- Flexible filtering by data source, event ID, message, and more
- Full event details including raw JSON payload
- Export raw data for external tools or compliance evidence
What can you do with Fencer's security monitoring capabilities?
Detect suspicious activity across your cloud infrastructure
AWS root credential usage, CloudTrail changes, unusual access patterns, failed authentication spikes. Fencer flags events that could indicate an attack in progress or a policy violation.
Satisfy SOC 2 monitoring requirements
SOC 2 and other frameworks require continuous monitoring, detection, and incident response capabilities. Fencer provides documented evidence that you're actively watching for threats, not just hoping nothing bad happens.
Investigate security events faster
When something looks suspicious, use threat hunting to search your logs, filter by time range or data source, and drill into the raw event data. No switching between cloud consoles or piecing together logs manually.
Monitor identity provider activity
1Password logins without MFA, geo-improbable access, unusual client detection. Fencer monitors your identity provider for signs of account compromise or policy violations.

“For a small team, Fencer is very simple to set up and gives you a lot of easy-to-use tooling. If you don’t have in-house security experts, it can go a long way to helping you run a successful cybersecurity program.”
— Jason Byck
CTO, Renew
Take Fencer for a spin
Start a free trial in minutes, or book a demo for a guided tour.