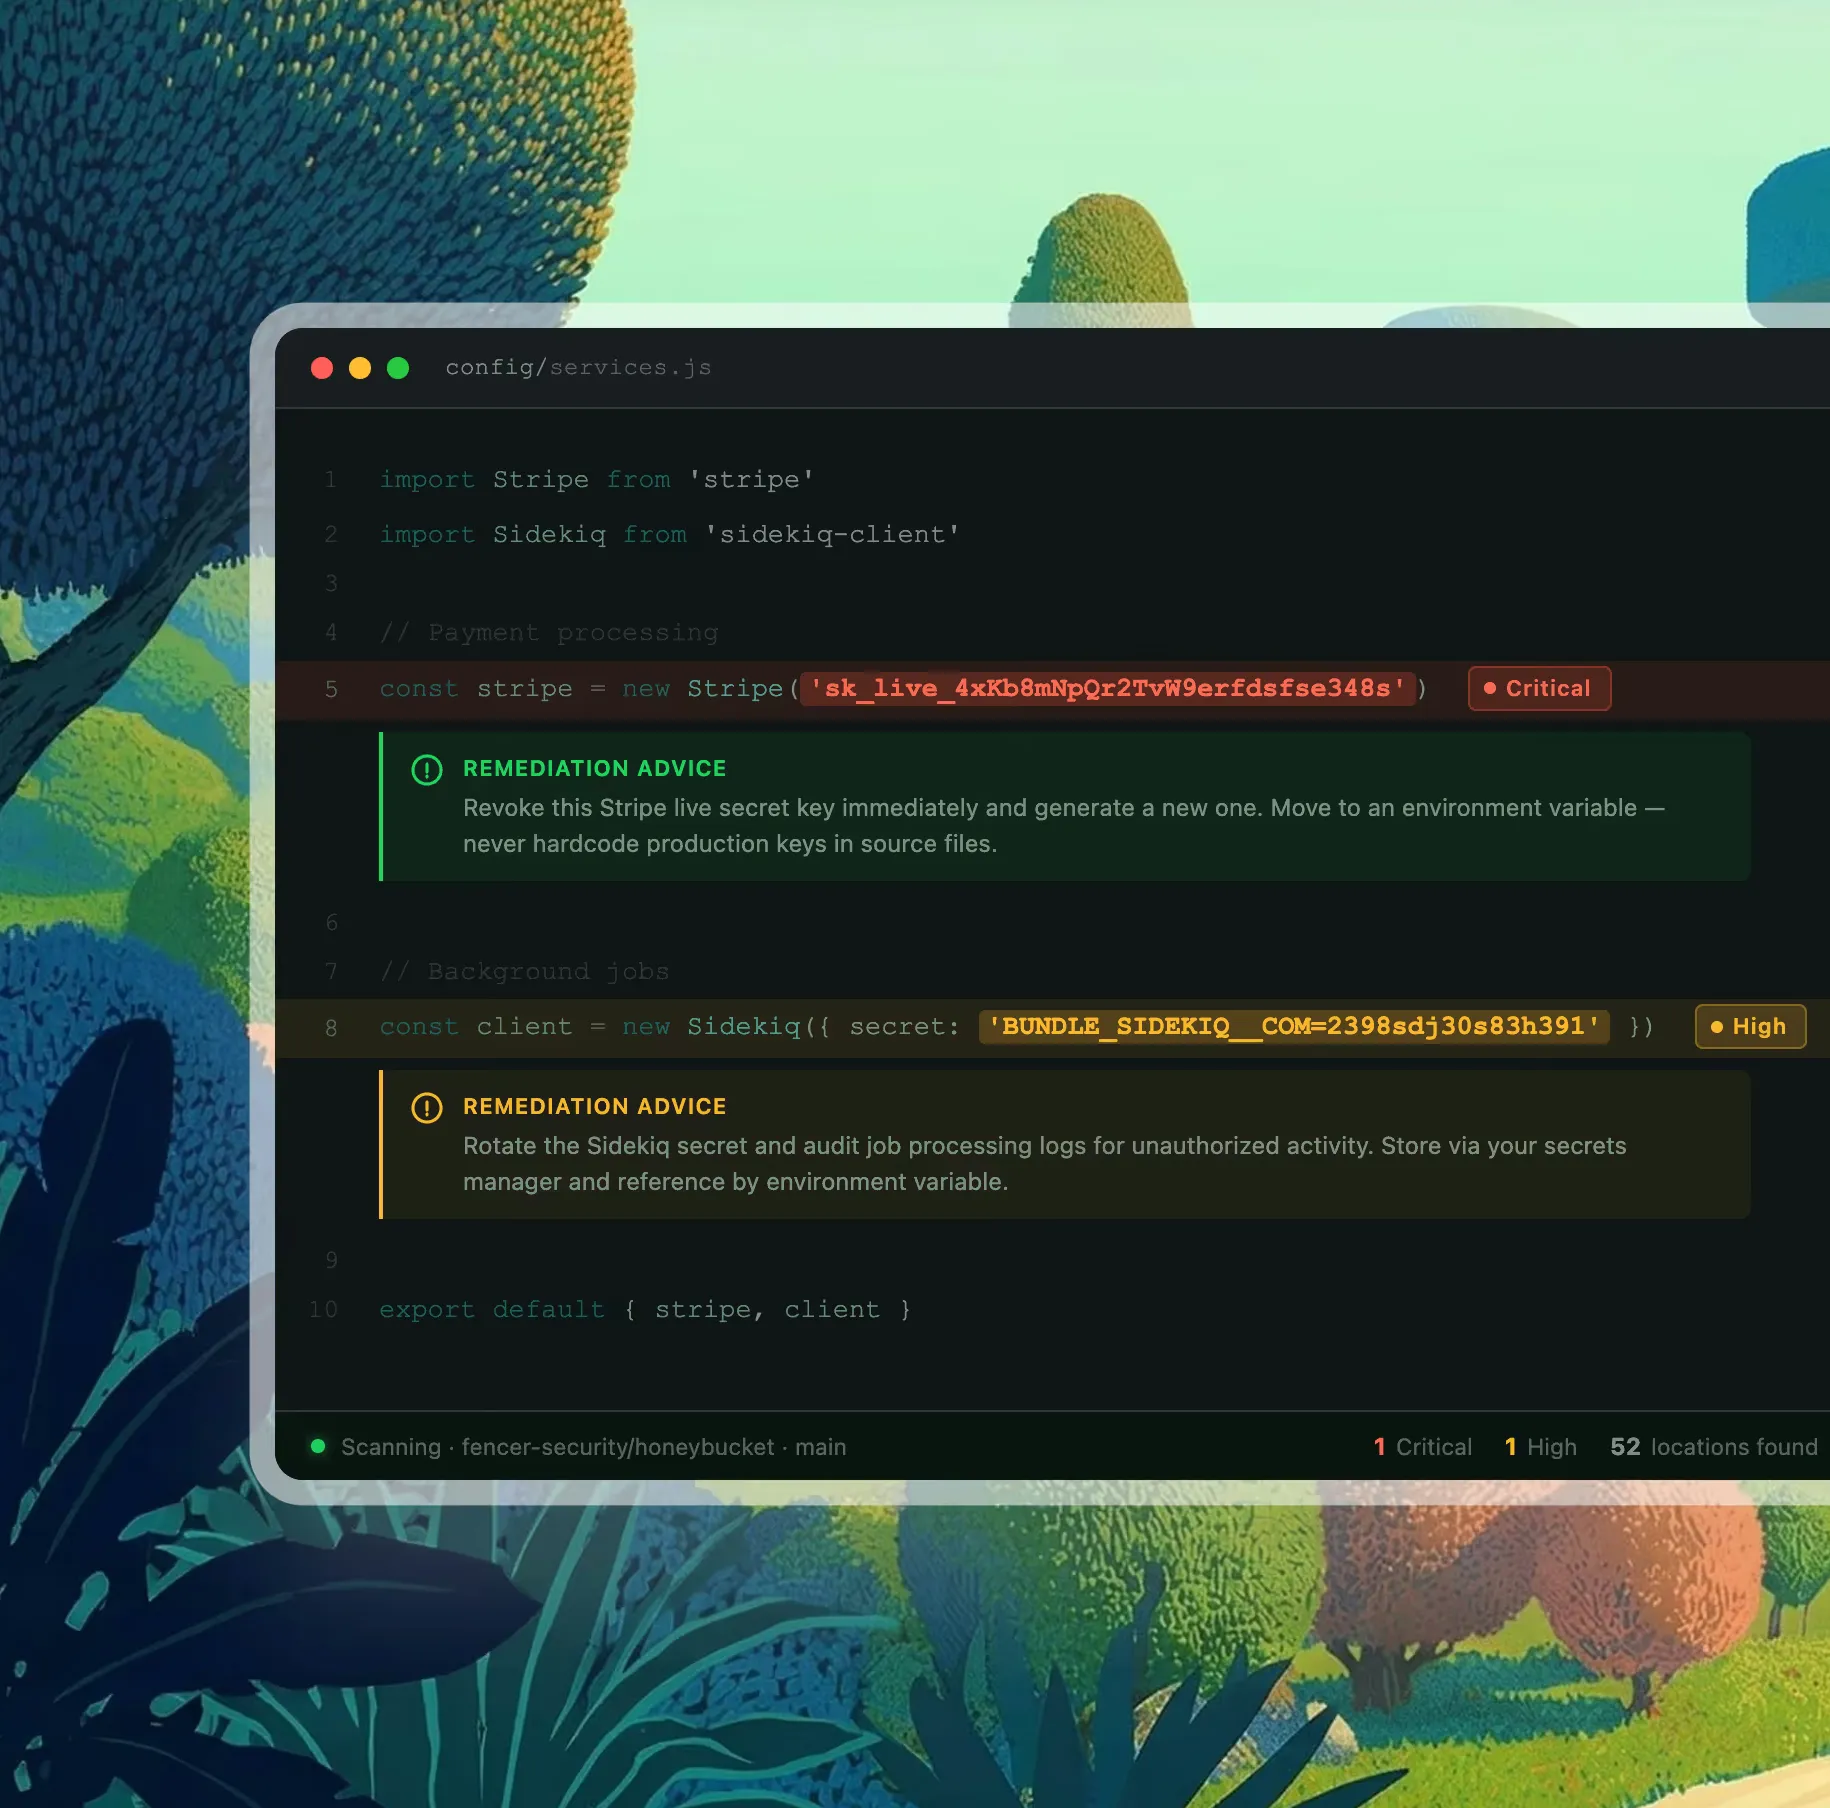
Secrets scanning for teams that can't afford a breach
Fencer scans your entire codebase and hosting platforms for exposed API keys, tokens, private keys, and hardcoded credentials. Every new pull request is checked automatically. Every finding comes with specific guidance on what to fix and how.
Why Fencer for Secrets Scanning
Secrets scanning for startups
Connect your repo and hosting platforms, and Fencer scans everything. Most teams find exposed credentials they didn't know were there.
Every finding comes with specific guidance on what to revoke, what to audit, and how to store credentials properly. No security team needed to act on it.
Secrets scanning sits inside a complete security foundation, not a standalone tool you manage separately. One platform, one workflow.
Capabilities
Surface hardcoded credentials before they cause damage
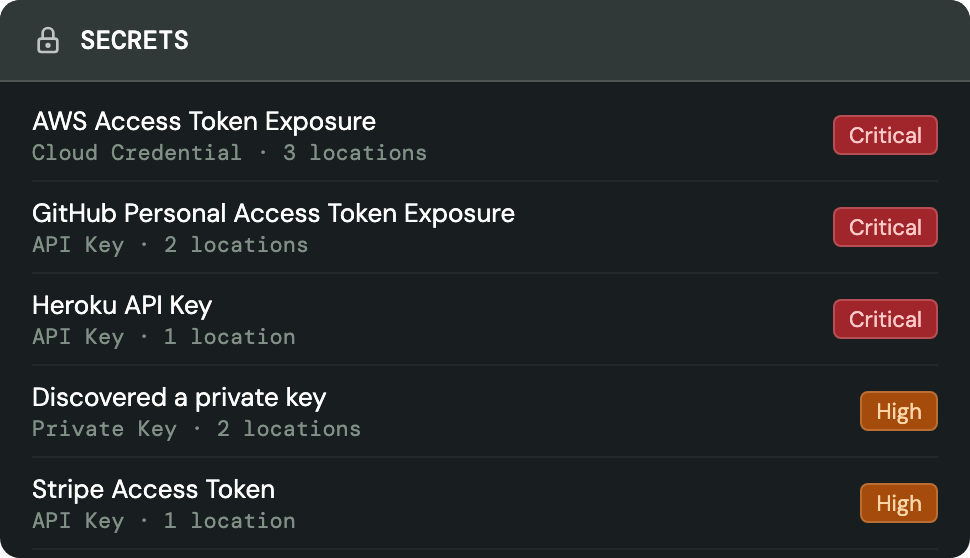
See every exposed credential across your code and hosting platforms
Fencer scans all of your existing code when you connect, and continuously checks every new commit going forward. It also scans hosting platforms including AWS, GCP, Azure, Heroku, Render, and Railway — so exposed credentials surface wherever they live.
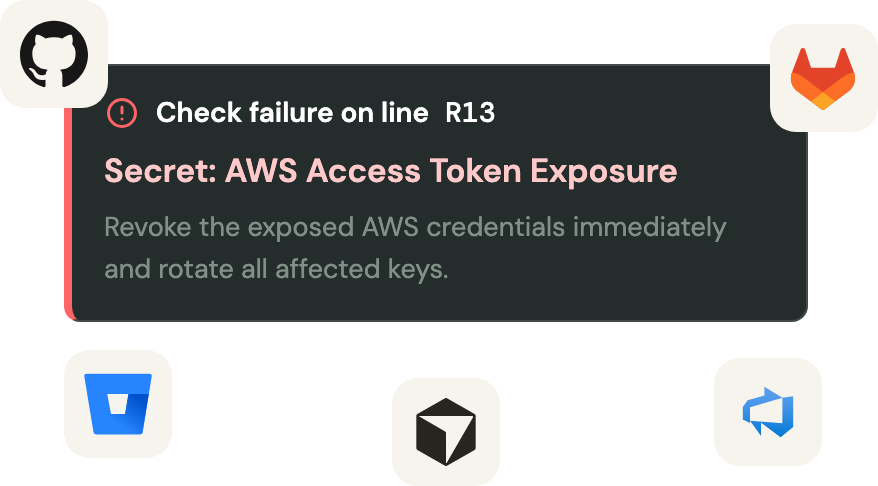
Catch exposed credentials in pull requests before they reach production
Every pull request is scanned for exposed credentials before it merges. Findings surface in your existing workflow, so secrets are caught at the point they're introduced.

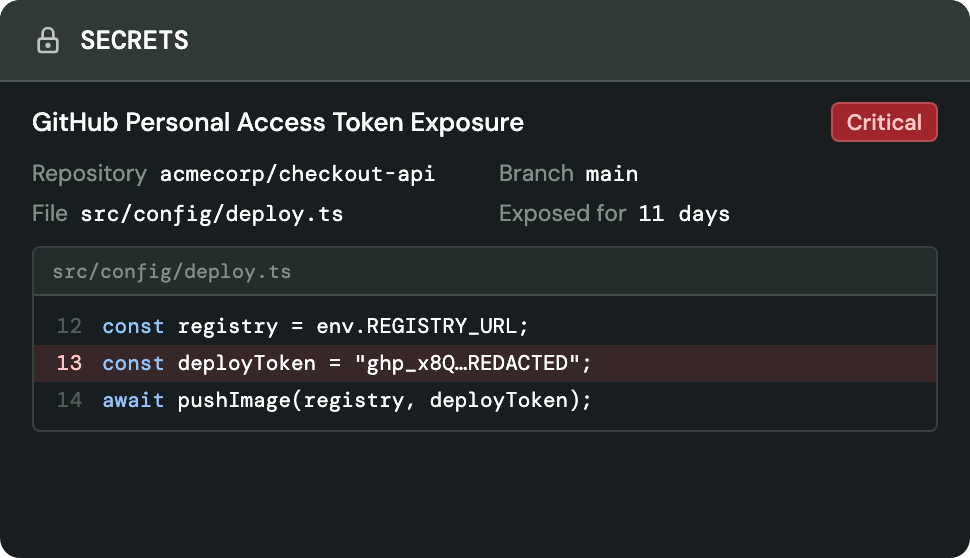
Know exactly where every exposed credential lives
Each finding shows the exact repository, branch, file path, and line of code where a credential was found, along with how many locations it spans and how long it has been present.
What can you do with Fencer's secret scanning capabilities?
Find credentials exposed in your existing codebase
Most teams find exposed credentials they didn't know existed when they first connect. Fencer scans your full codebase on day one, not just code going forward.
Catch exposed secrets before they reach your main branch
Pull requests are scanned before they merge. You catch exposed credentials in your existing workflow before anything reaches production.
Satisfy SOC 2 credential monitoring requirements
SOC 2 and other major compliance frameworks require evidence of active credential monitoring, not just policy.
Respond to an exposed credential before it causes damage
When a secret is flagged, Fencer shows exactly where it is, how long it has been exposed, and what to do next.

“As a small startup, Fencer gives us a lot more comfort and tools that we otherwise wouldn’t have to ensure our product is secure.”
— Jason Byck
CTO, Renew
Take Fencer for a spin
Start a free trial in minutes, or book a demo for a guided tour.