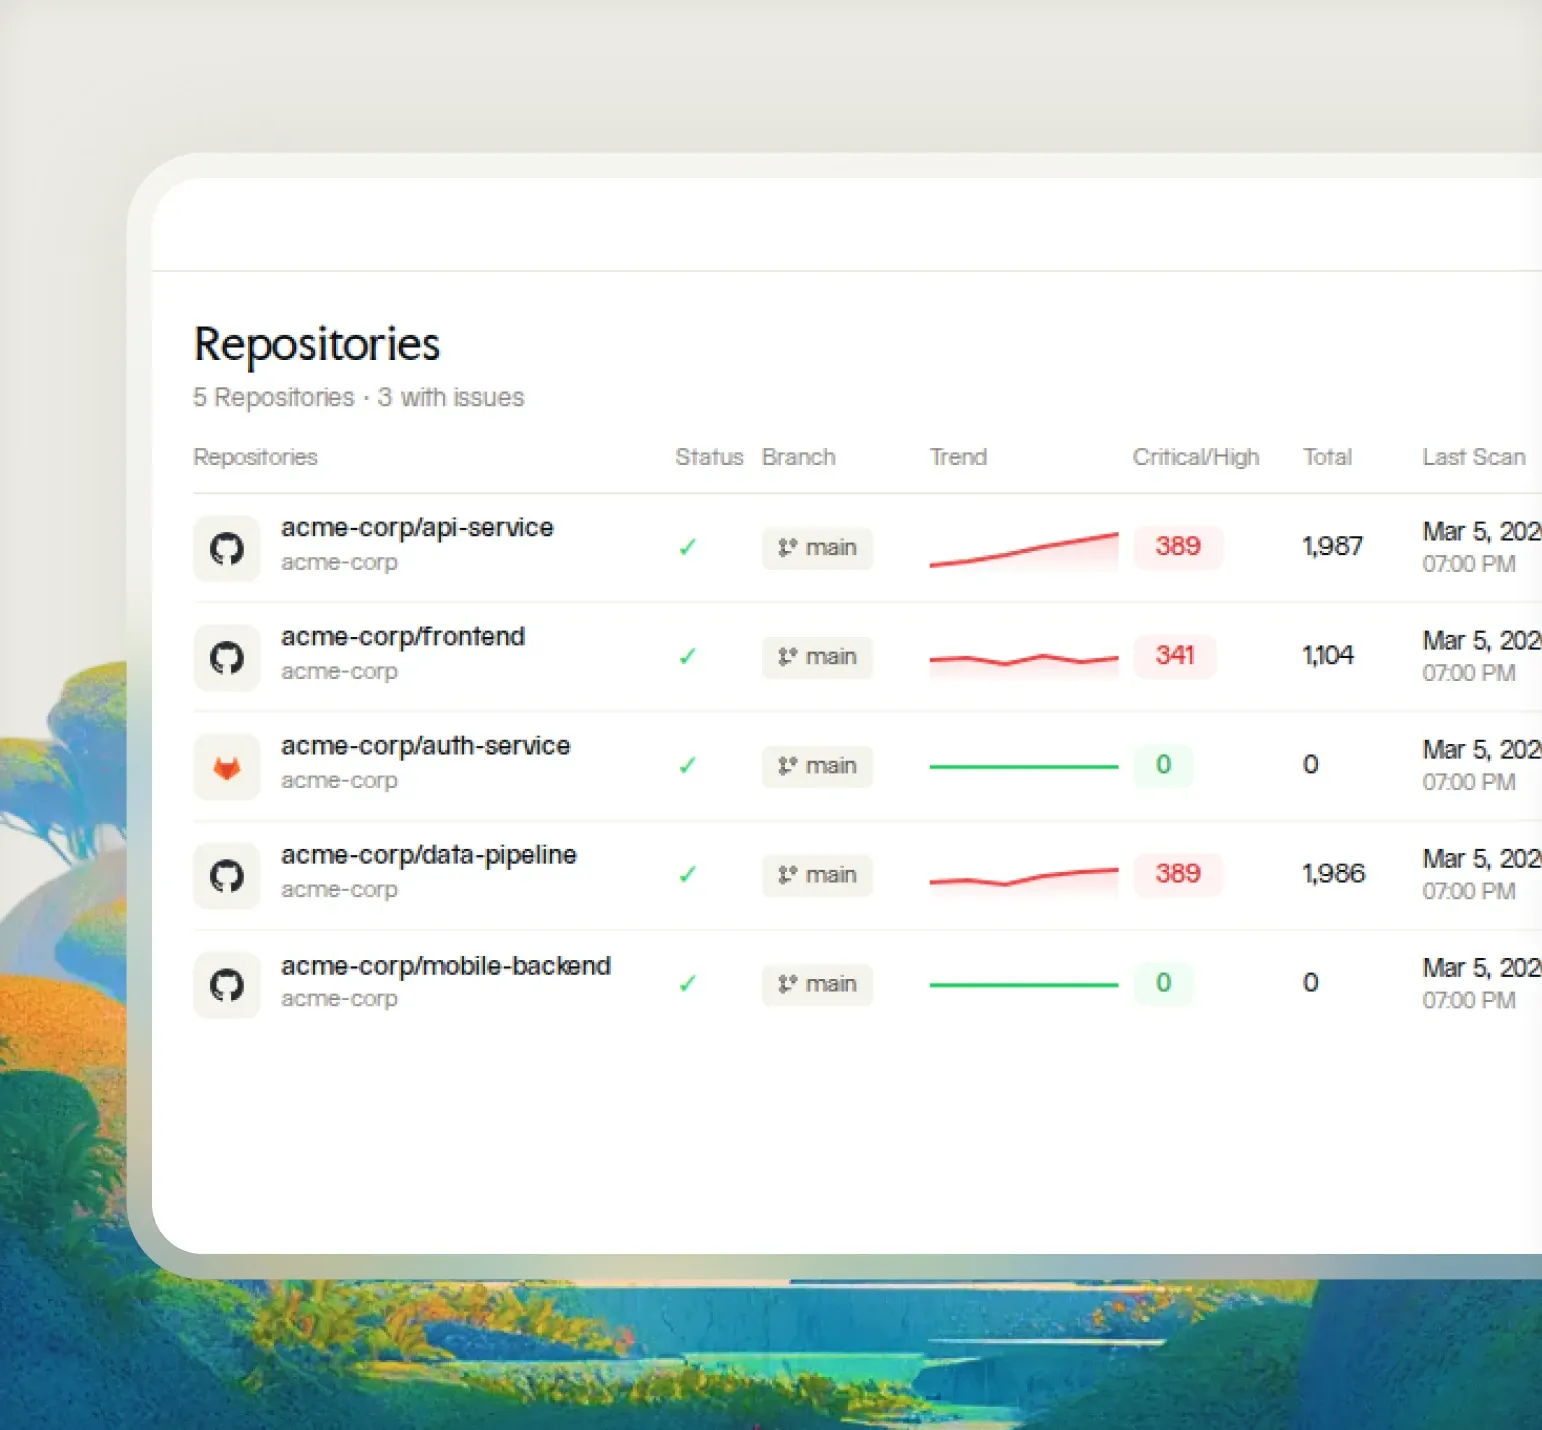
Code scanning that finds and fixes vulnerabilities
Fencer runs PR security checks on every pull request across all your repositories, flagging vulnerabilities, exposed secrets, and dependency risks before they merge, and generates AI-powered fixes you can ship in one click. Connect GitHub, GitLab, or Bitbucket and get your first scan results in minutes.
Why Fencer for Code Scanning?
Ship secure code faster
Connect your repos and get your first scan results without configuration or a security engineer. No rules to write, no pipelines to wire up.
Most tools find vulnerabilities and stop there. Fencer flags them in the PR, generates an AI fix, and opens the pull request to ship it.
Code security is one part of a complete security foundation alongside vulnerability scanning, identity, infrastructure, and more. One platform, for all your security essentials.
Capabilities
Code scanning features
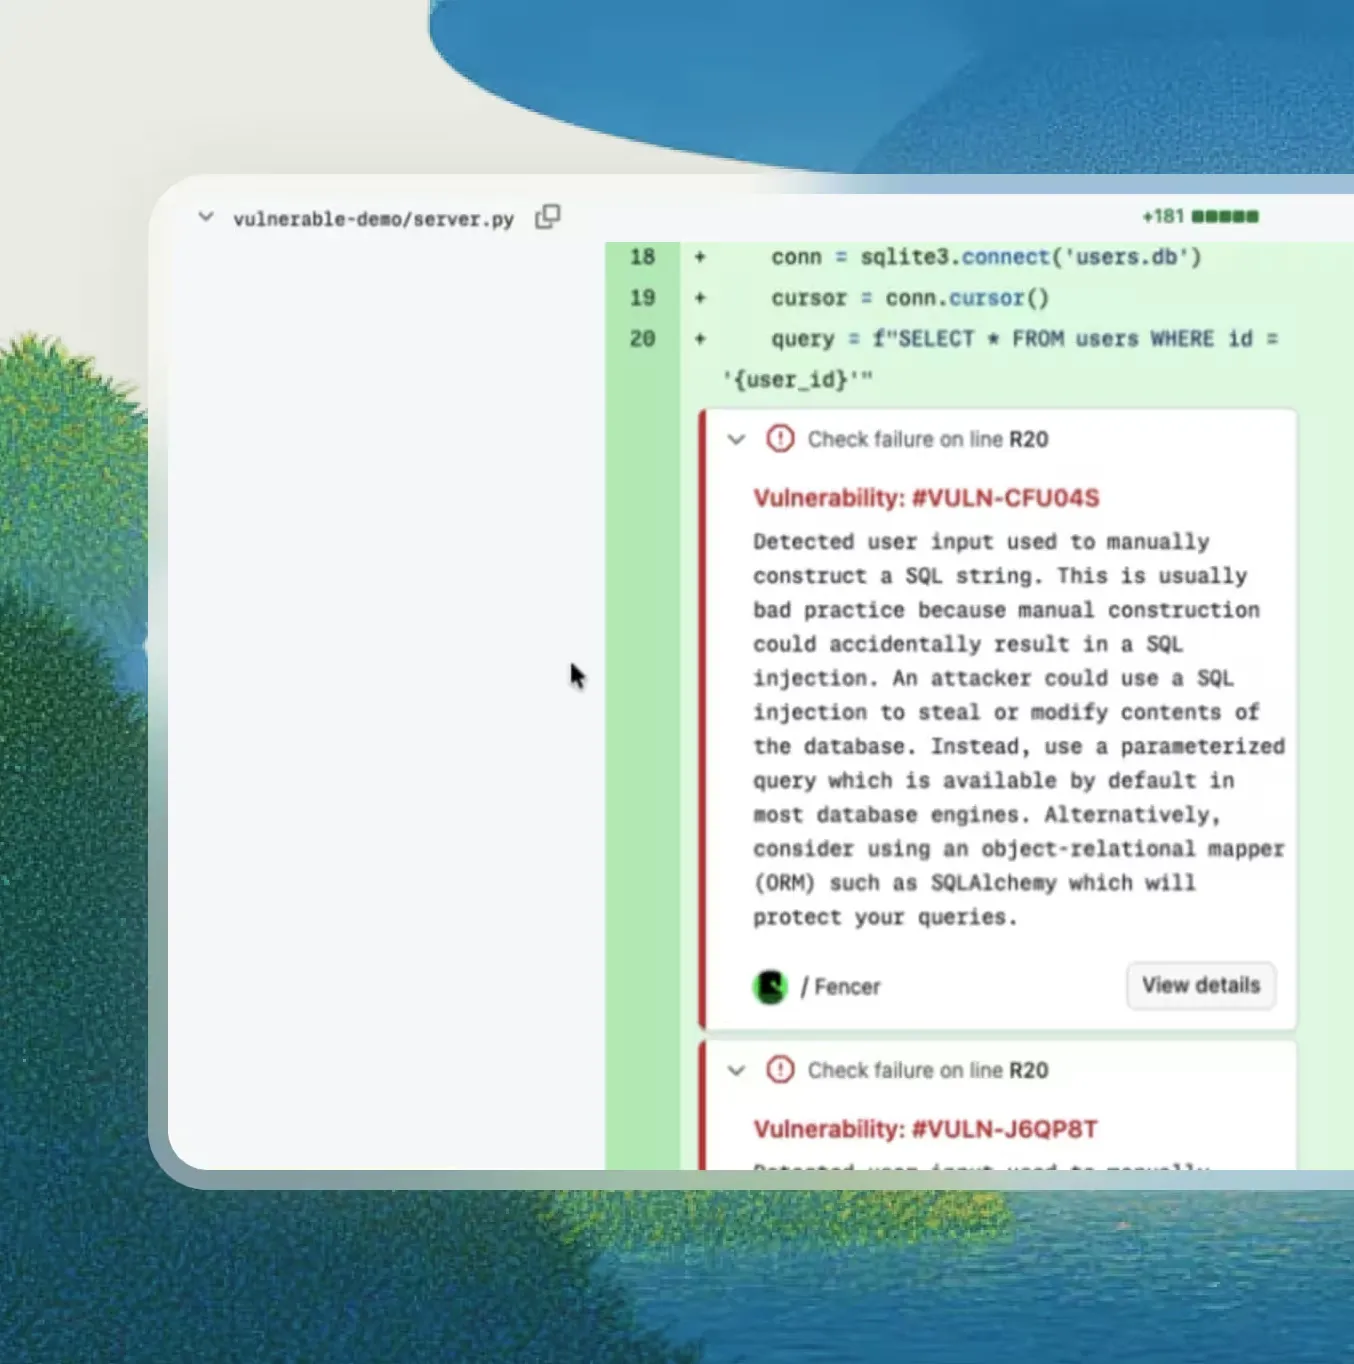
PR security checks on every pull request
Fencer runs as a native check on every pull request, surfacing security issues directly in the PR so you can fix them before merging.
- Native PR scans: Fencer appears directly in your PR workflow
- New vs existing: Every scan distinguishes what this PR introduced from preexisting vulnerabilities
- Configurable thresholds: Set exactly what triggers a warning: severity level, new secrets, EOL packages, license risk etc.
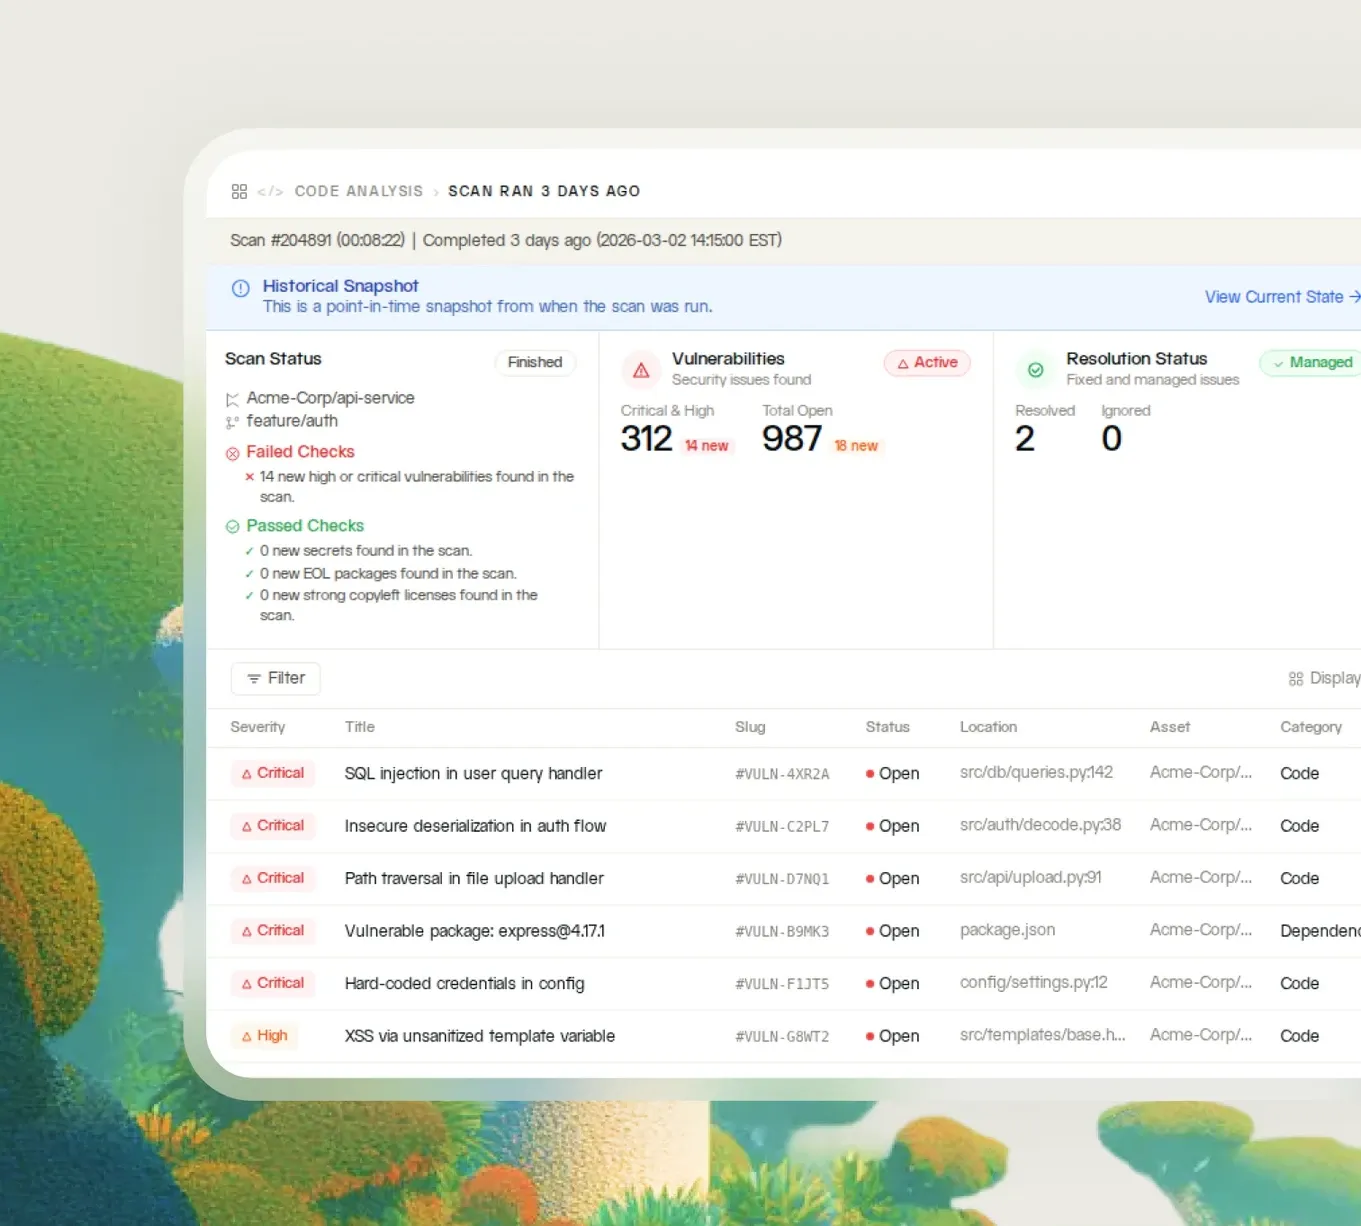
Static code analysis across all major languages
Fencer's SAST engine scans your source code on every PR and on a daily schedule, catching security vulnerabilities before they reach production. Covers all major languages with no configuration required.
- Severity levels (Critical, High, Medium, Low) so you know what to fix first
- Scan history with timestamp, trigger type, and the name of who initiated it
- Assignable findings with issue tracking integration for accountability
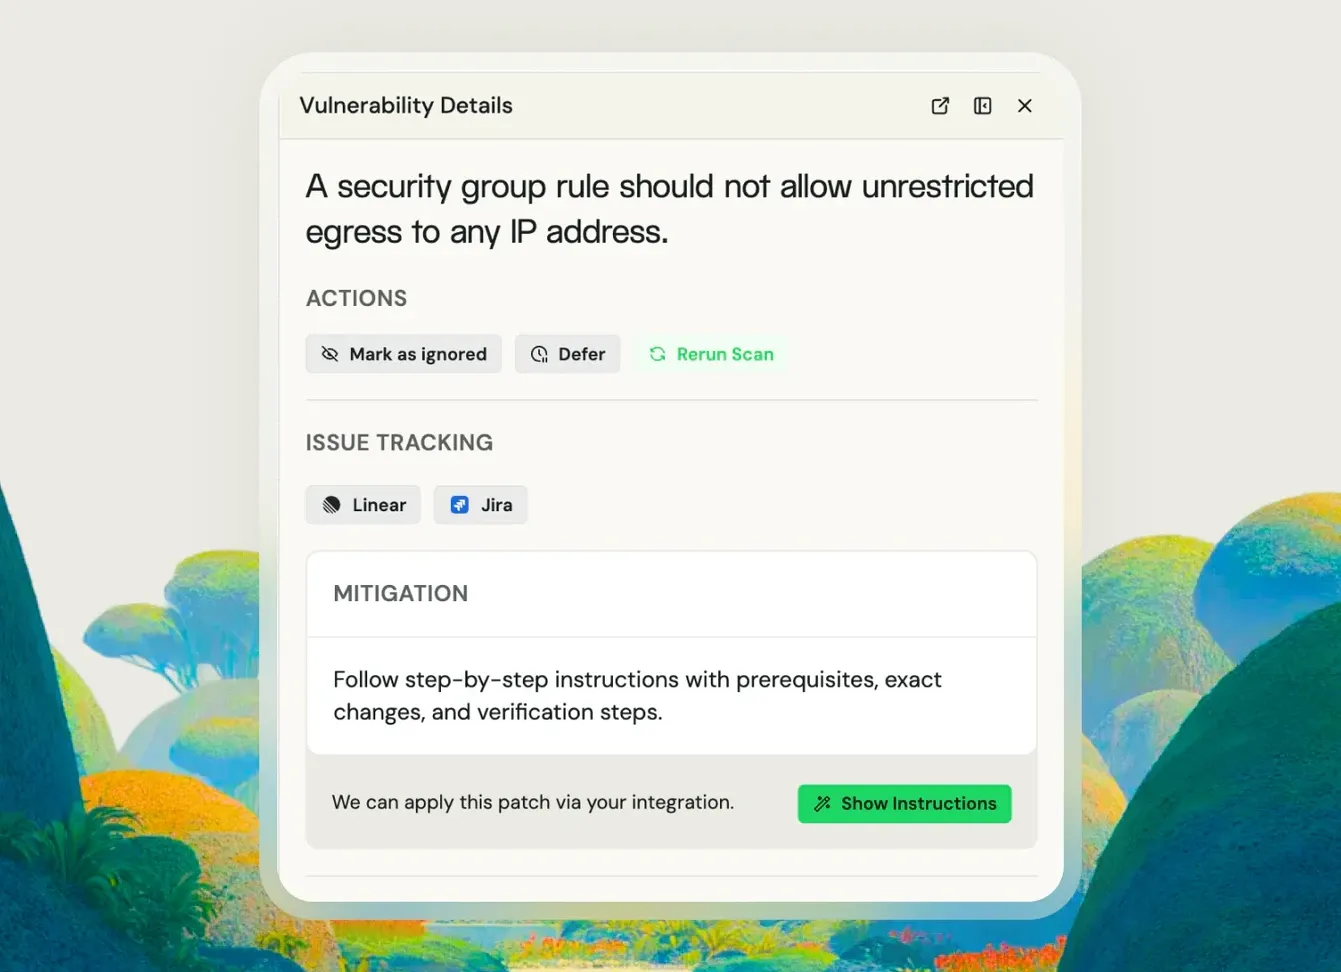
Go from vulnerability found to vulnerability fixed in one click
When a finding needs fixing, Fencer launches an AI agent that generates a patch and opens a pull request. Resolve security findings without leaving your workflow.
- Works across finding types: code vulnerabilities, dependency issues, secrets, and more
- Full explanation included: summary of what changed and why, not just a diff
- PR created in your repo: one click from finding to fix
What can you do with Fencer's code scanning capabilities?
Catch vulnerabilities in your CI/CD pipeline before they ship
Fencer scans every pull request automatically and surfaces issues before they reach main. No security expertise required on the reviewing team.
Build a code scanning program that satisfies compliance requirements
Compliance auditors want evidence of a running code security program, not just a policy that says you do code reviews. Fencer's scan history and resolution tracking give you that record from day one.
Earn enterprise trust
Enterprise customers ask about your application security program before they sign. Fencer gives you a real answer: automated scanning on every pull request, across all repos, with compliance evidence that builds continuously.
Remediate vulnerabilities without a dedicated security team
Fencer's AI fix agent analyzes the issue, generates a patch with a full explanation, and opens a pull request in your repo. Your developer reviews it and merges it, no security expertise required.

“Every PR that is opened by an engineer will have a Fencer review on it, and that review will call out security holes and security opportunities that the engineers then fix on the spot, ensuring those vulnerabilities never make it into our code.”
— Ari Baranian
Co-founder & CEO, Pirros
Take Fencer for a spin
Start a free trial in minutes, or book a demo for a guided tour.