Know your open source risk with software composition analysis
Fencer scans every connected repository and builds a live dependency inventory with license risk scoring, dependency graph visualization, and SBOM export in CycloneDX or SPDX.
Why Fencer for SCA
SCA for startups
Connect your repositories, and Fencer starts building your dependency inventory immediately. When a CVE drops or an auditor asks, the answer is already there.
Rules for AWS, GCP, 1Password, and GitHub are ready out of the box. Each includes remediation guidance so you know what to do when something fires.
Fencer covers the security essentials startups need. SCA is part of a broader platform covering application infrastructure, access, and monitoring.
Capabilities
Everything you need to know about your open source dependencies
Complete dependency inventory across all your repositories
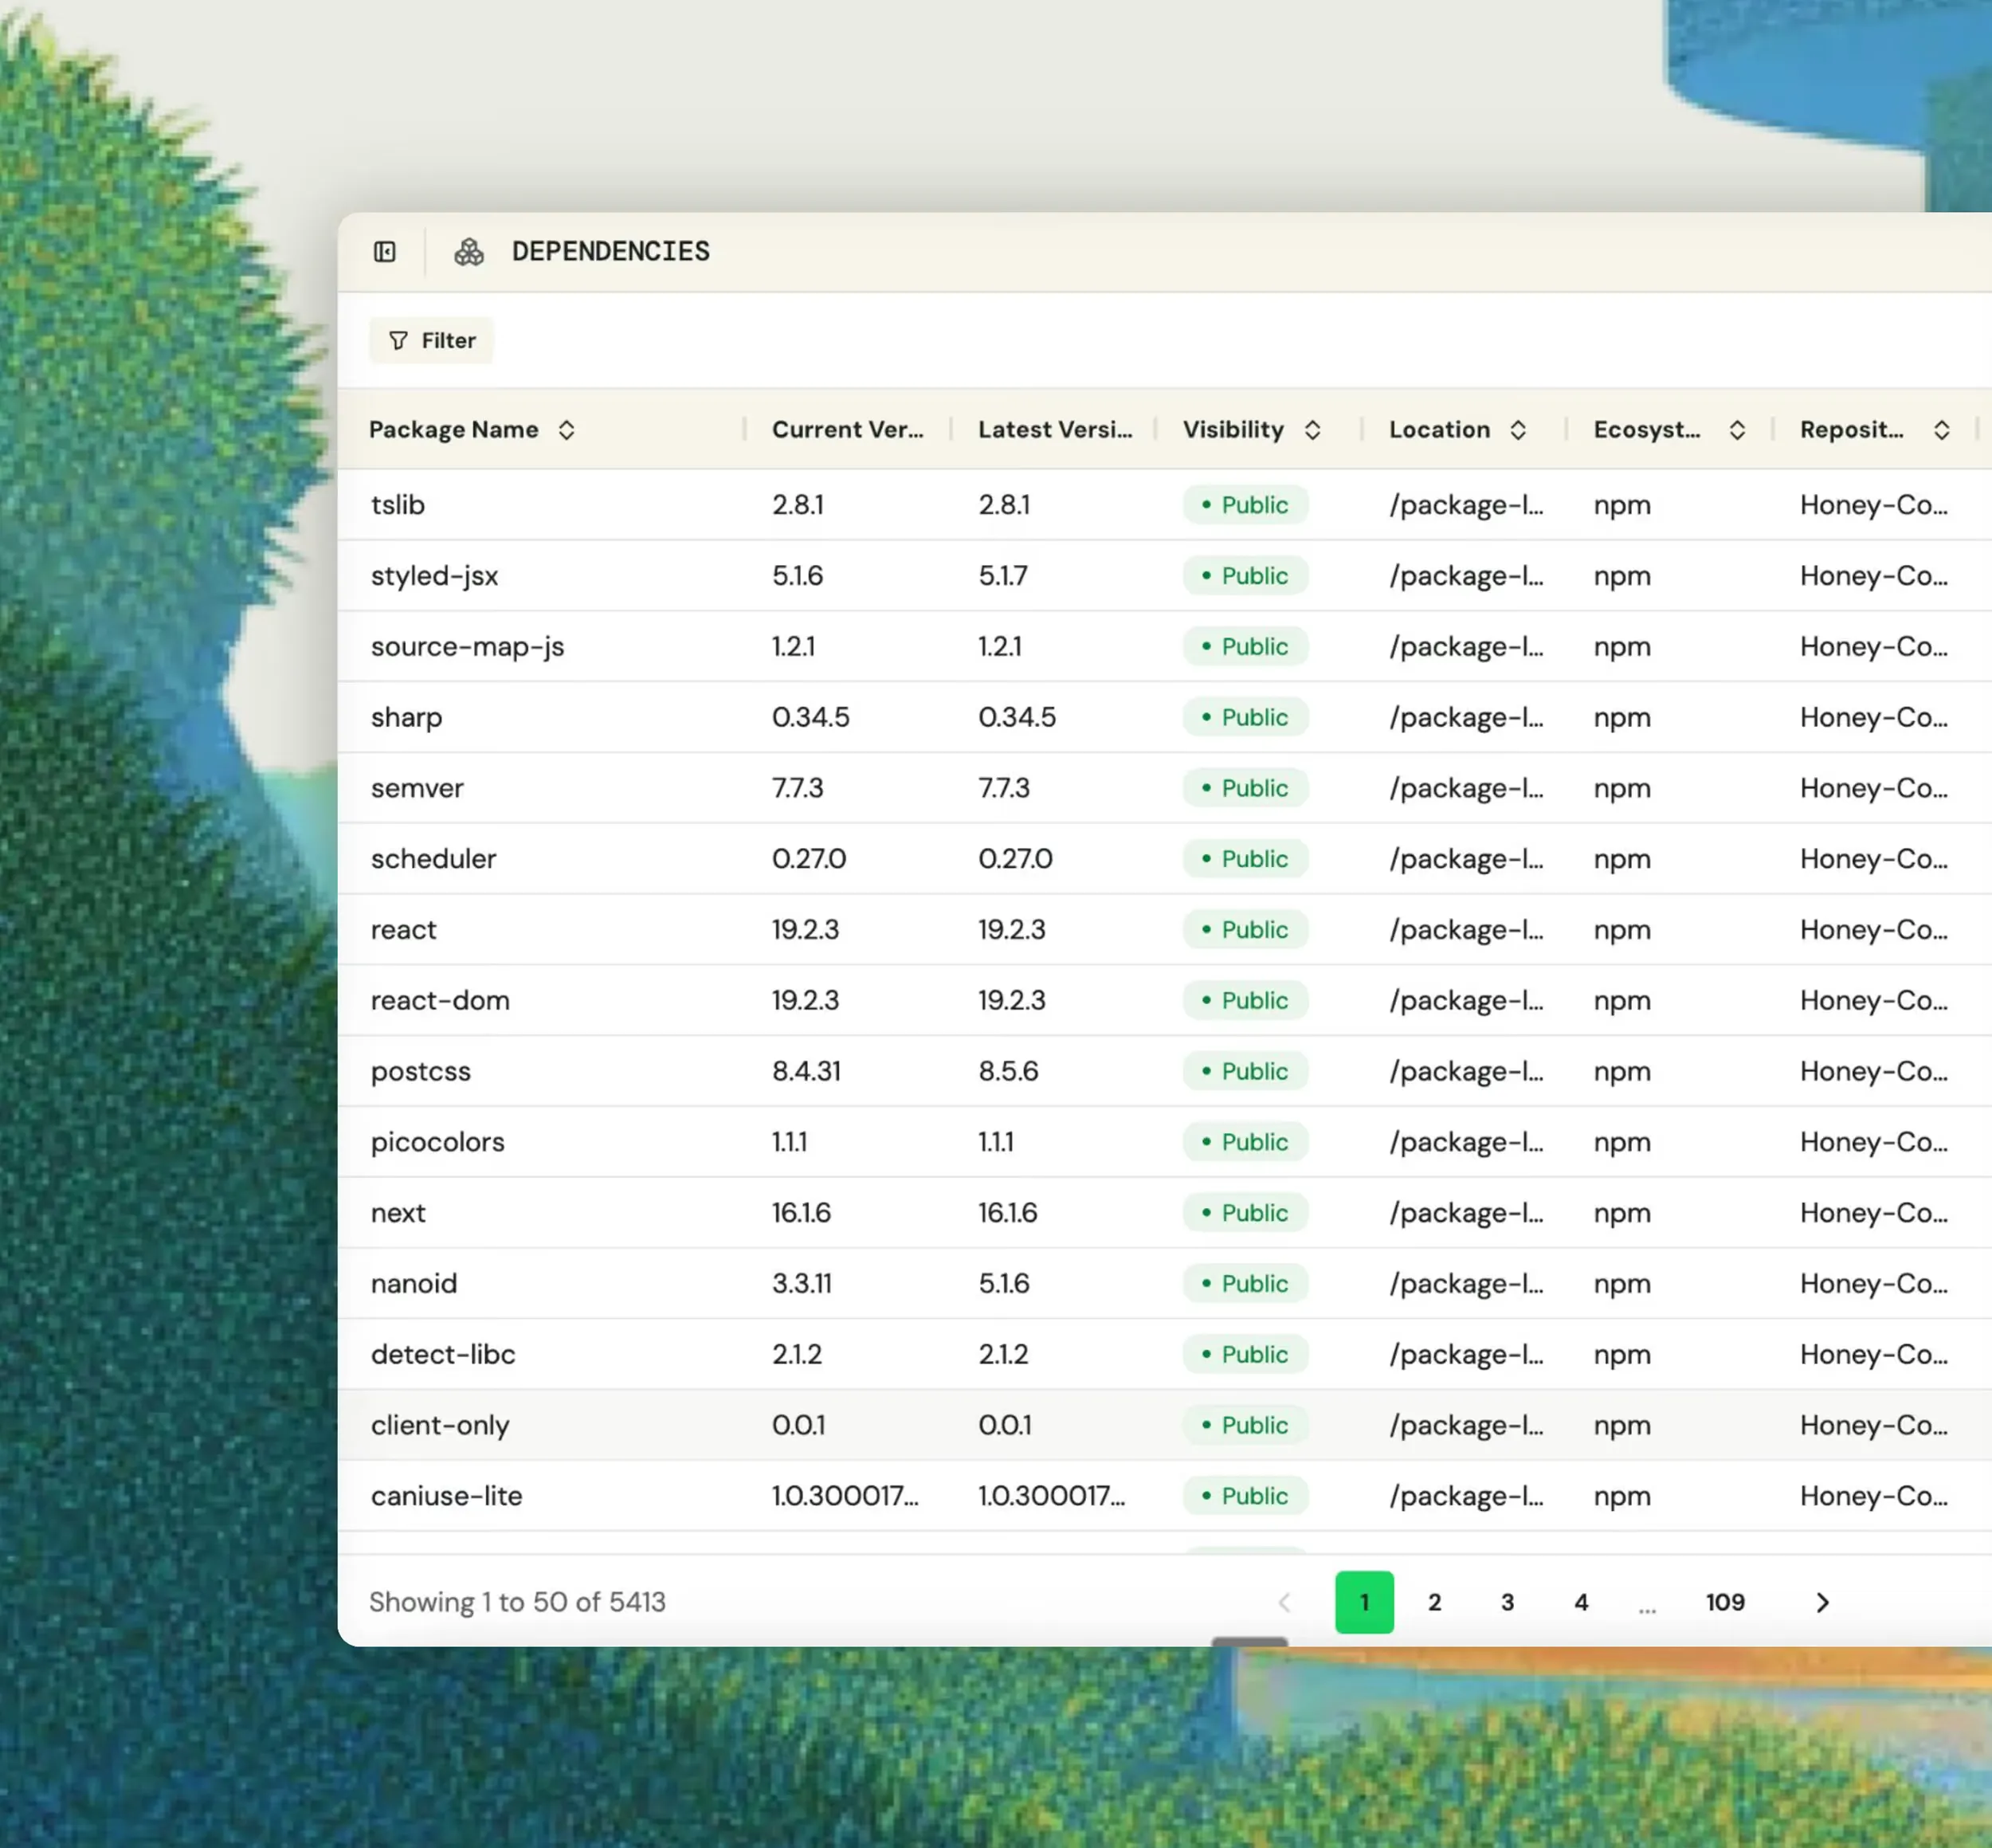
Fencer scans every connected repository and surfaces every dependency (direct, transitive, and root) in a searchable, filterable list. When a CVE drops, you know which repositories are affected before you have to go looking.
- Package name and version: Current version and latest available shown side by side
- Ecosystem and location: Which package manager and which file the dependency lives in
- Repository and branch: Full asset context so you know where each dependency is used
- Dependency type: filter by route, direct, or transitive dependencies
- First seen timestamp: track when dependencies entered your stack
Understand your full dependency exposure
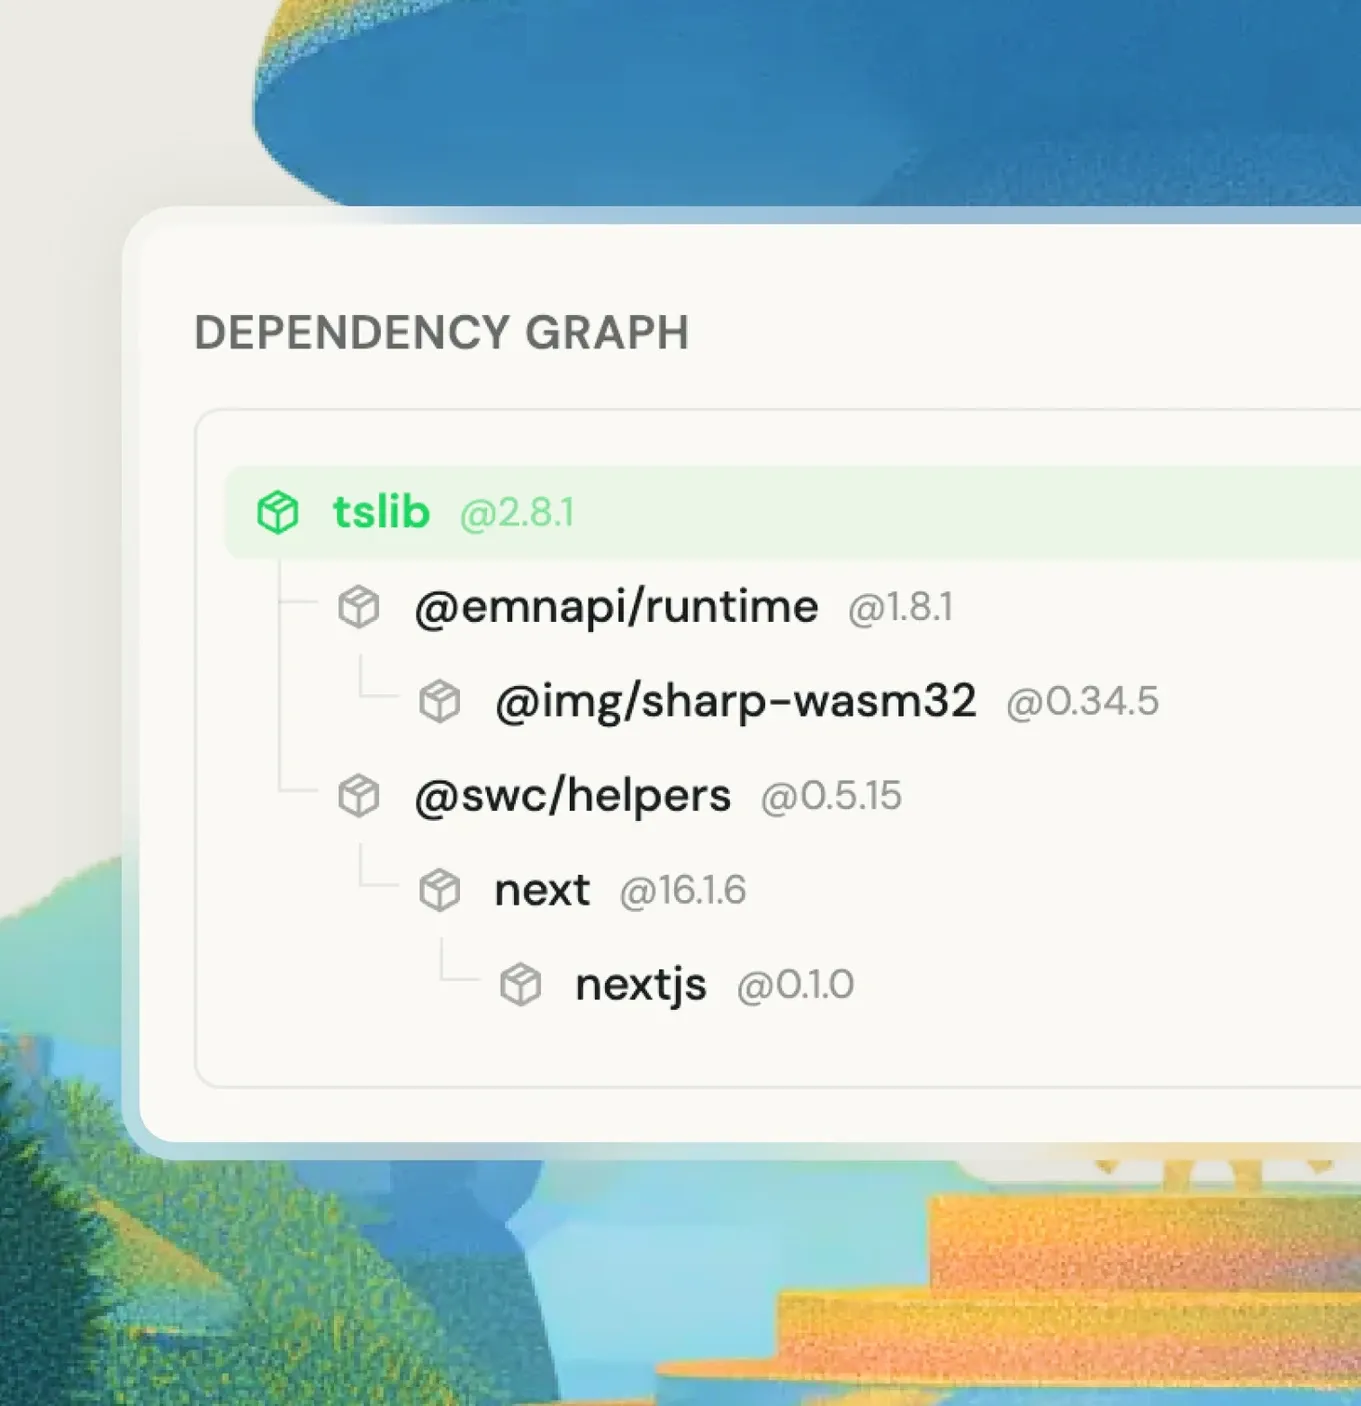
Fencer maps how every dependency relates to the rest of your stack, including what transitive dependencies it pulls in. When a vulnerability or license issue surfaces in a shared package, you can see the blast radius without digging through manifests.
- Parent-child tree view: See which packages depend on which
- Transitive dependency coverage: Packages your packages depend on, fully mapped
- Blast radius visibility: Understand how far a single problematic dependency reaches across your stack
SBOM generation in CycloneDX and SPDX formats
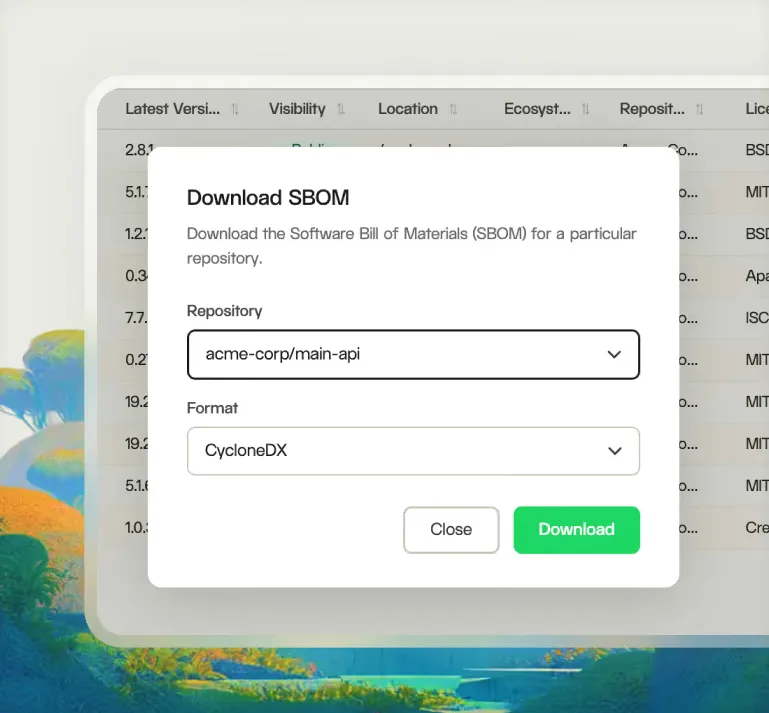
Generate a software bill of materials for any connected repository on demand, in Cyclone DX or SPDX format. When a customer, enterprise prospect, or auditor requests a software inventory, you can produce it in seconds.
- Cyclone DX and SPDX formats: The two most widely accepted SBOM standards
- Per repository export: Download an SBOM for any specific repository from the dependencies view
- On-demand generation: No scheduled jobs or manual build steps required
What can you do with Fencer's software composition analysis?
Respond to a new CVE in minutes
When a critical vulnerability is disclosed in a popular open source package, Fencer's dependency inventory shows you which repositories are affected so you can triage and act fast.
Produce an SBOM for a customer or auditor
Enterprise prospects and compliance auditors increasingly ask for a software bill of materials before signing a contract or completing an assessment. With Fencer, you can generate one on the spot in the format they need.
Catch license risk before it becomes a legal problem
Strong copyleft licenses like GPL can create unexpected obligations in a commercial codebase. Fencer flags them early, before they can become a problem.
Demonstrate open source controls for compliance
Most major compliance frameworks expect organizations to track and document their open source components. Fencer gives you a documented, always current inventory that supports your audit evidence without manual effort.

“For a small team, Fencer is very simple to set up and gives you a lot of easy-to-use tooling. If you don’t have in-house security experts, it can go a long way to helping you run a successful cybersecurity program.”
— Jason Byck
CTO, Renew
Take Fencer for a spin
Start a free trial in minutes, or book a demo for a guided tour.