For Govtech
Security for govtech startups
Strong security for public-sector systems and sensitive data, without slowing down product delivery or burying engineers in process.
Govtech startup security challenges

Selling to government agencies brings strict security requirements early.

Compliance certification frameworks like CMMC and FedRAMP raise the bar for technical controls and documentation.

Engineers inherit security work alongside shipping features for demanding customers.

Enterprise security platforms assume dedicated teams and long security deployment timelines.

Agencies need confidence your systems are secure, stable, and well-governed.
How Fencer helps govtech startups
Built into the workflows engineers already use to build and ship software.
Security coverage maps to the technical requirements those frameworks expect.
Surface the issues that matter instead of flooding teams with low-value alerts.
Evidence, findings, and security context stay current as part of day-to-day work.
Security essentials for govtech startups
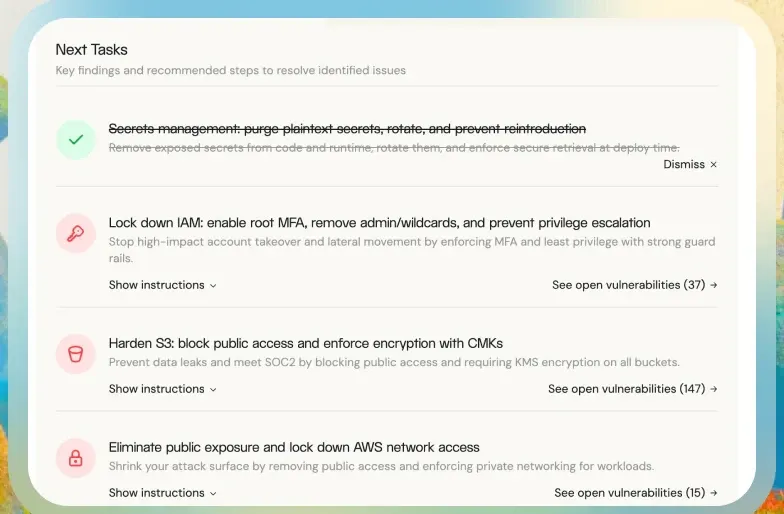
Vulnerability Detection

See security issues in one place instead of chasing alerts across tools.
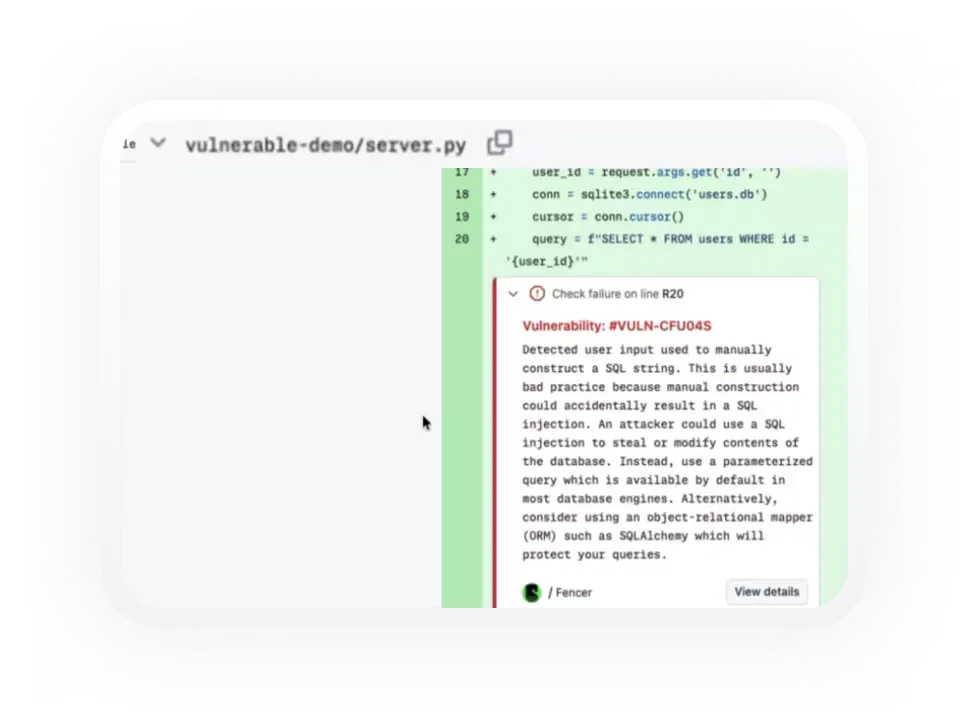
Code Scanning
Find issues before they ship.
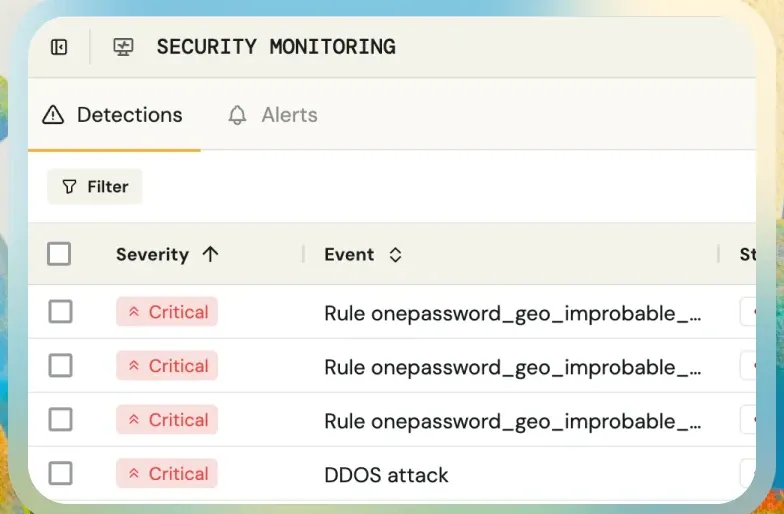
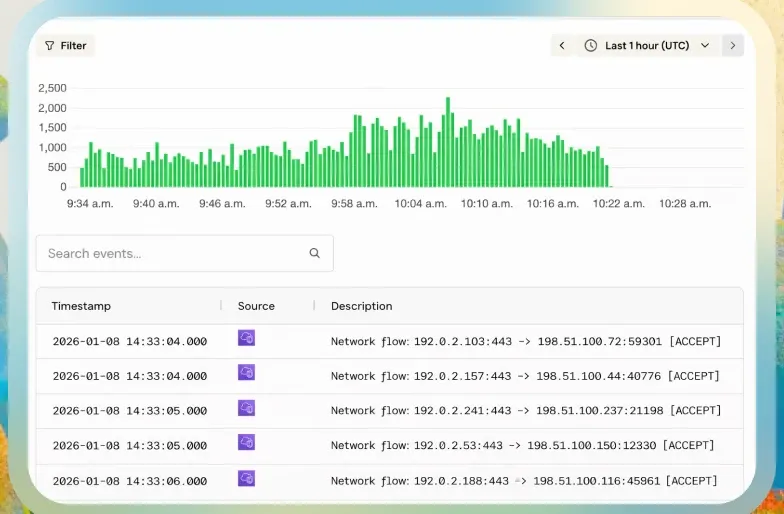
Integrated SIEM
Understand what's happening without running a full security operations team.
Threat and Incident Management
Respond to document issues clearly for internal response and external review.
Compliance integrations
Auto-generate evidence to support your CMMC and FedRAMP assessments and sync directly to your GRC tool of choice.

“Most security tools are built for teams much larger than ours. Fencer made it possible for a small engineering team to take security seriously without adding complexity or overhead.”
— David Merrit,
CTO, Watch Duty
Take Fencer for a spin
Start a free trial in minutes, or book a demo for a guided tour.