Procurement readiness check
Pressure-test your SOC 2 report against your buyers’ security requirements
A clean SOC 2 gets you in the door, not past what enterprise security teams ask next. Upload your report, tell us who’s buying, and see where you’d fall short before a deal stalls.
WHO BUILT THIS
"In every CTO role I’ve had, security eventually became my job. A SOC 2 was never what got us through a buyer’s security review. This is the tool I wish I’d had then."Learn About Fencer →Reviewed the way your buyers will review it
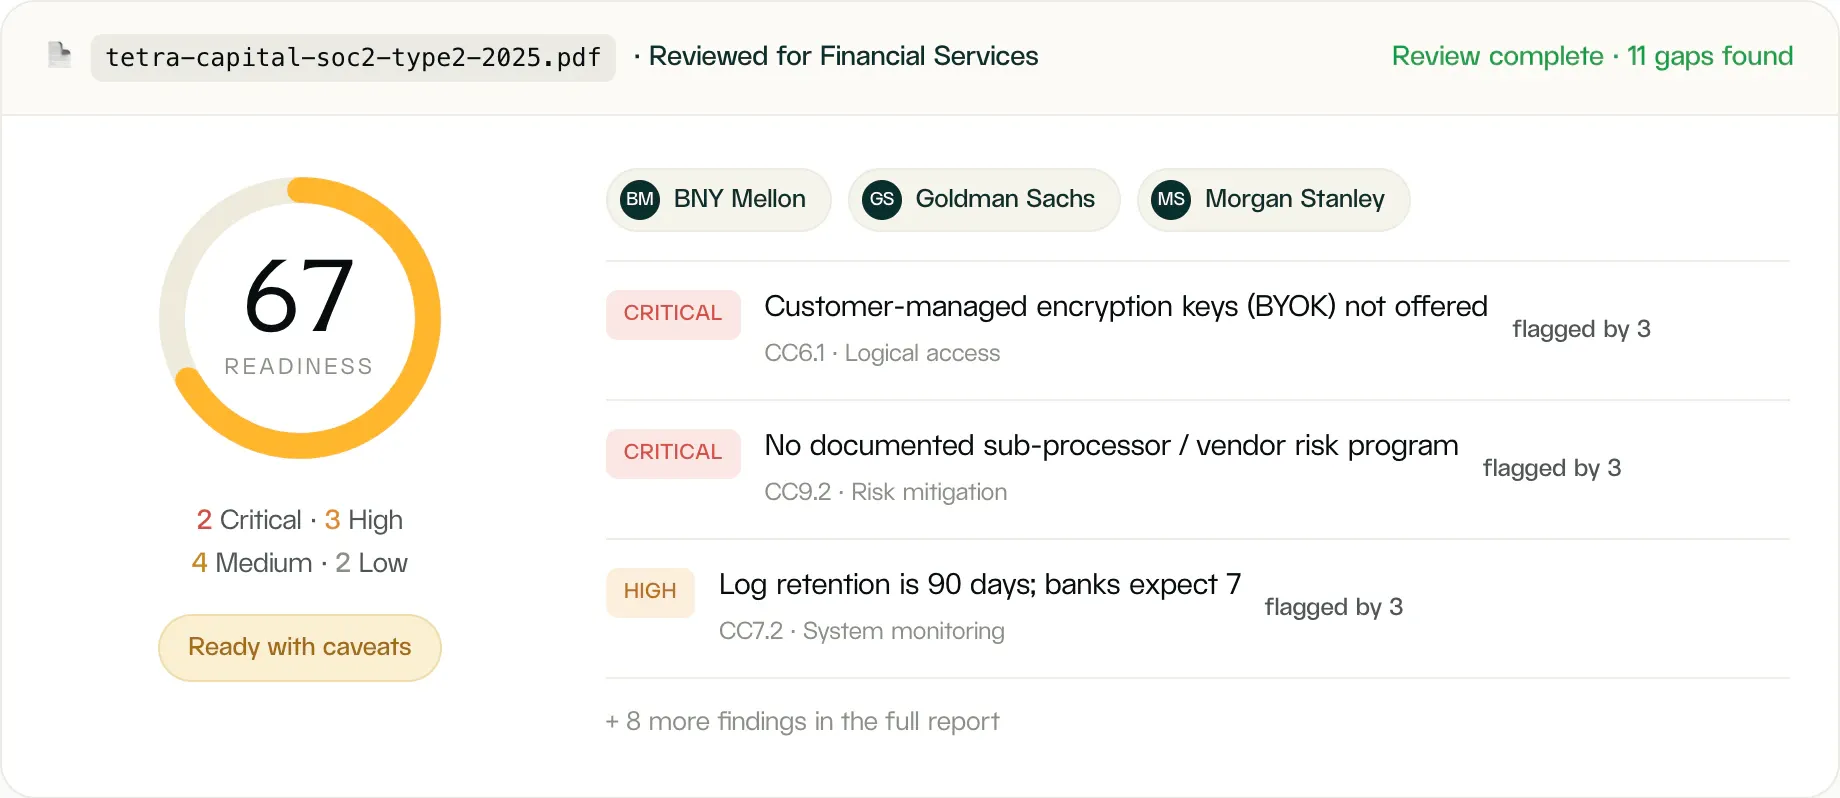
Name your real target accounts and we read your report the way each of their security teams would. Every finding shows how many of your named buyers would flag it.
Why a clean SOC 2 isn’t enough
The certificate proves you checked the boxes
Buyers want proof you did the work
SOC 2 is table stakes now, common enough that enterprise reviewers trust the badge less than the evidence. Their questionnaires and risk tools dig past the certificate into specifics like key custody, retention windows, and pen-test cadence. Identify where your report comes up short while you can still fix it, not in the middle of a stalled deal.
How it works
From PDF to procurement-ready in three steps
01
Upload your SOC 2
Drop the PDF. We extract every control, assertion, and CUEC.
02
Tell us who’s buying
Industry, size, and named accounts. We calibrate the review to those buyers.
03
Get your readiness report
Your controls versus what buyers expect: what’s strong, what they’ll flag, and how to fix it. Secure link sent to your work email.
What we check
The same questions your buyers will ask
We pattern-match against the real questionnaires, MSA schedules, and frameworks enterprise buyers run, not the SOC 2 standard in the abstract.
Encryption & key custody
CMK/BYOK, key rotation, revocation
Vendor risk program
Sub-processor tiering, annual review evidence
Logging & retention
Audit-log immutability, 7-year retention
Pen-test cadence
Frequency, scope, retest after critical findings
Incident response
Customer-facing SLAs, IR commander, post-mortems
Identity
SSO + SCIM auto-deprovisioning, MFA enforcement
Business continuity
Live failover evidence, multi-region commitments
Personnel screening
Annual re-screening for prod-access engineers
Data residency
Contractual region commitments, notice windows
Software supply chain
SBOM, dependency provenance, build attestation
Privacy
Your report is handled with care
✓
Confidential by default
Access limited to authorized Fencer personnel, only to operate the service.
✓
Never used for training
Your report and its contents never train our models.
✓
Encrypted in transit and at rest
Including while held in memory during the review.
✓
Deleted after review
Files and parsed contents aren’t kept beyond the session.