SOC 2 security testing

Pen testing for your SOC 2, handled today

Get a pen test plus all the vulnerability scanning your auditor expects, for just $3000.

The problem

Your compliance platform stops where the testing starts

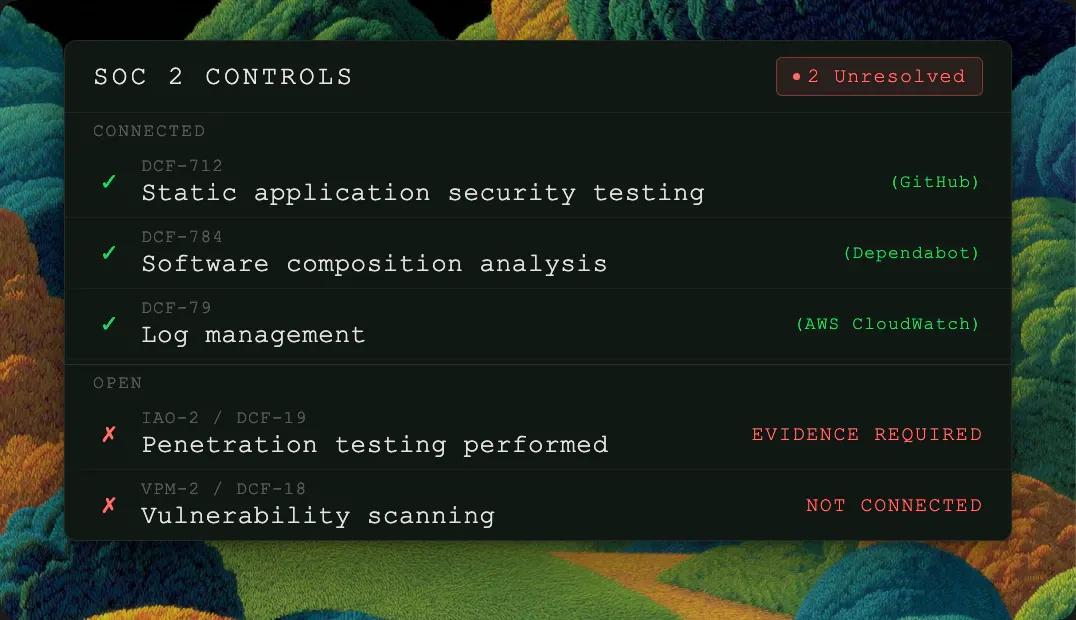
Vanta and Drata told you to turn on GuardDuty and Dependabot. The gap they don't fill is the one your auditor cares about most: a pen test and external vulnerability scans of your actual attack surface.

An open door standing alone in a field.

The solution

From setup to audit-ready report, in hours

Fencer covers your pen test, network scanning, and domain monitoring, continuously, so you're ready for any audit or security review.

PDF
northwindlabs.dev Fencer Agent Penetration Test
Scoping
Penetration test lifecycle.
Scoping
9:14 AM
Scheduled
9:14 AM
In progress
9:31 AM
Ready for remediation
1:42 PM
Completed
2:47 PM
Details
9
Test configuration
Vulnerabilities
0
Waiting to start
Attack chains
0
Confirmed paths
Artifacts
0
Evidence
Severity
Title
Status
3 selectedLinear
Vulnerability Details
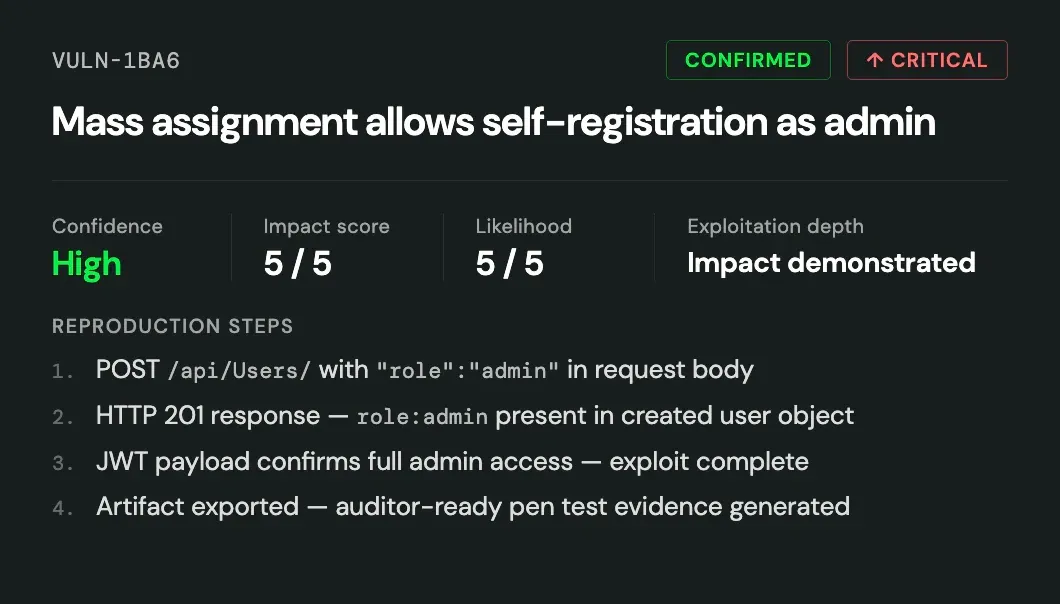
Mass assignment allows self-registration as an admin user
VULN-1BA6
 CriticalConfirmed
PROOF OF CONCEPT
POST /api/v1/users/ {"email":"attacker@example.com","role":"admin"}→ HTTP 201role:admin present in created user object
REPRODUCTION STEPS
1.POST /api/v1/users/ with "role":"admin" in the request body alongside a valid email and password
2.Server responds HTTP 201; the created user object echoes role:admin, confirming the field was mass-assigned
3.Authenticate as the new user via POST /api/v1/auth/token; the issued JWT carries "role":"admin"
4.Call GET /api/v1/admin/billing/ with the token; the admin-only endpoint returns HTTP 200
IMPACT
Any unauthenticated visitor can create an administrator account and take over the tenant. With admin access an attacker can read every tenant's billing records, manage users, issue API keys, and persist beyond remediation of this endpoint. Confirmed against staging with billing data for all four tenants returned.
ART-118 · response capture attached to the report
Linear
CreateLinkUnlink
Select a team
Pick a team first
Pick a team first
Pick a team first
Cancel
Create Issues
Pen test evidence synced to Vanta

01

Connect your stack

Link your infrastructure in minutes; Fencer maps what needs to be covered.

02

Scope and run a pen test

Fencer probes your application and surfaces exploitable vulnerabilities, delivering your audit-ready report in hours, not weeks.

03

Monitor continuously

Network and domain scanning runs in the background, flagging new issues as they emerge.

04

Stay audit-ready

Evidence is organized and accessible when your auditor or a customer's security team asks for it.

What you get

Automated security testing designed for teams without a security team

Auditor-accepted pen test results, in hours

Fencer chains weaknesses into a full attack path and proves the exploit end to end, so your report holds up in an audit.

From finding to fixed, in one loop

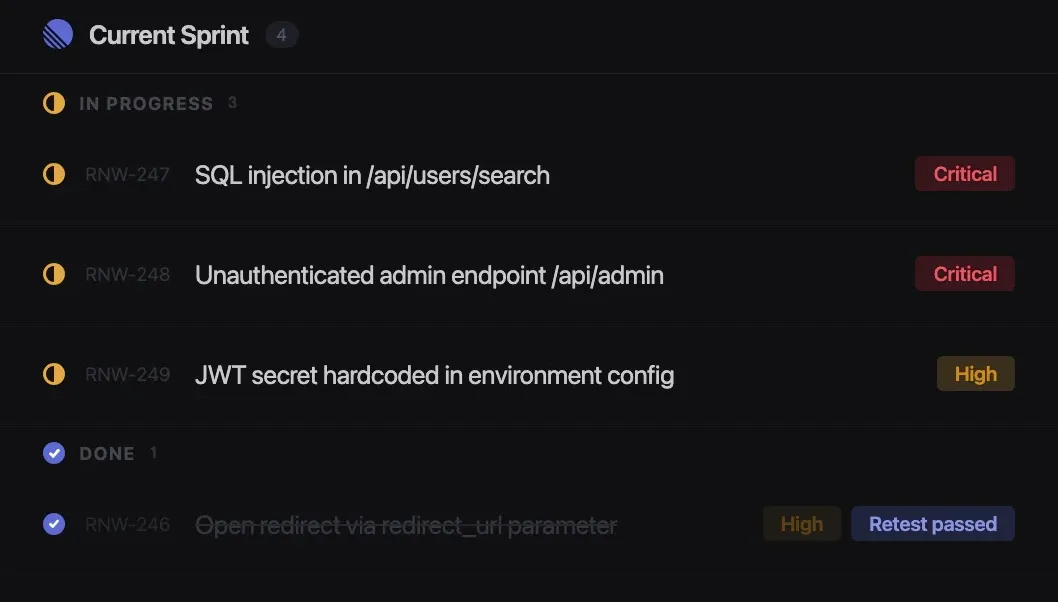
Findings land in your issue tracker with remediation guidance. Fix, retest, confirm it's closed, all without buying another test.

Fencer pen test findings synced to Linear as sprint issues

Evidence that follows your workflow

Results and scan history sync automatically into Vanta, Drata, or Secureframe. Export everything on demand when a customer's security team asks.

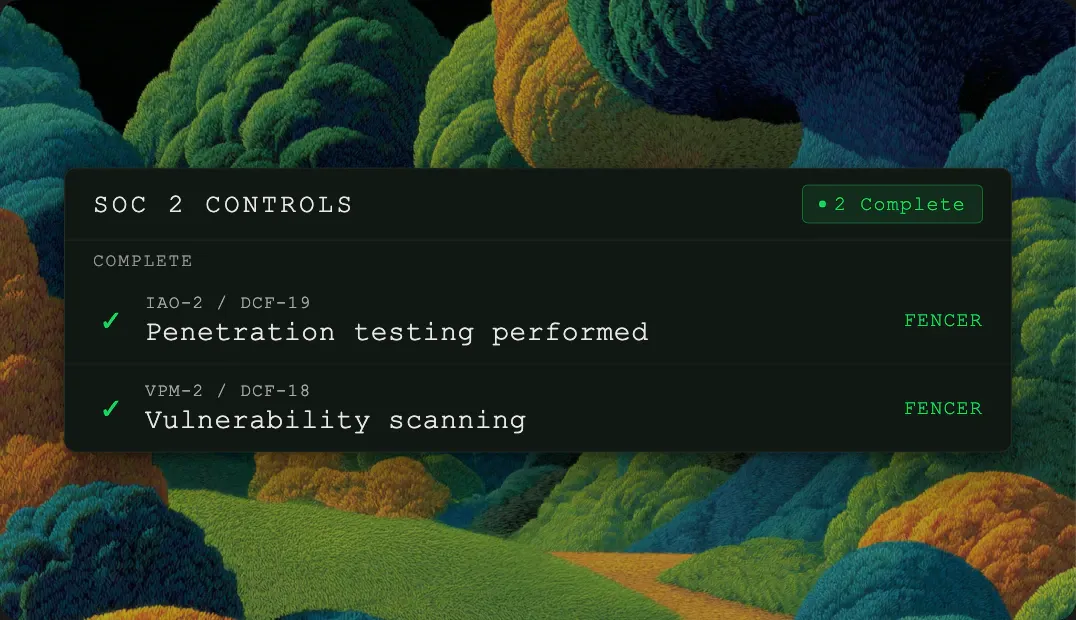
Two more checklist items, no second purchase

Setting up the pen test puts network scanning and domain monitoring in place at the same time.

Pricing

Cover more than you planned, pay less than you expected

Point solutions

Fencer

Annual pen test

$5–$15K/yr

Included

On-demand pen test

Network vulnerability scanning

~$4K/yr

Included

Continuous network scanning

Domain monitoring

~$5K/yr

Included

Domain exposure monitoring

GRC evidence sync

Not included

Included

Evidence sync to Vanta, Drata, Secureframe

$14,000–$24,000

/ yr

$3,000

/ yr

Scope Pen Test

Testimonials

Companies that got audit-ready without a dedicated security team

Renew logo

Managing pentest findings used to eat up tons of our time. We'd parse reports, manually file tickets, build trackers, and then coordinate the retest. With Fencer, findings go straight into Linear with everything our team needs to act on them. Remediation becomes part of the normal sprint instead of a project on top of it.

Justin Rhoades

Justin Rhoades

Director of Engineering

RTOPilot logo

A customer asked for pen test evidence. We ran Fencer's AI pen test, got findings with accurate severity and clear remediation steps, and handed them the report. It replaced what would have been a full third-party engagement.

Manning Blackall

Manning Blackall

Co-founder

Fontana logo

Fencer's AI pen testing delivered precise and easy-to-understand results that I was able to action immediately. As a solo founder, the service was invaluable and exactly what I needed from a security tool.

Gabriel Garayalde

Gabriel Garayalde

Founder

Common questions about SOC 2 pen testing for SMBs

Will my auditor accept an AI pen testing report from Fencer?

Yes. SOC 2 doesn't specify pen testing methodology. What auditors evaluate is evidence quality: the full attack path showing how vulnerabilities chain into a working exploit, documented methodology, severity ratings, and an attestation letter formatted for auditor review. Fencer's report covers all of those.

In some cases, your auditor may request a human co-review. If that happens, Fencer offers this as an add-on: a credentialed security engineer reviews findings and co-signs the report.

How long does a pen test take to complete?

Most pen tests complete within hours. The exact time depends on scope (the number of endpoints, application complexity, and depth of coverage), but for a typical SaaS application, you can scope, run, and receive your findings the same day.

Once scope is defined, Fencer begins immediately. The report includes the full attack path showing how findings chain into exploitable vulnerabilities, severity ratings, and an attestation letter formatted for your auditor or a prospect's security team.

How is Fencer different from Vanta, Drata, and Secureframe?

Vanta, Drata, and Secureframe automate compliance evidence collection. They connect to your infrastructure and SaaS tools, monitor whether controls are configured correctly, and organize the documentation your auditor needs to see. Security testing is outside their scope: no penetration test, no network scanning, no domain monitoring.

Fencer covers that piece. An AI pen test probes your application and surfaces exploitable vulnerabilities. Network scanning and domain monitoring run continuously alongside it. Your compliance platform tracks your progress toward a certificate; Fencer provides the evidence that your controls hold under pressure.

Many teams use both. If you're already on Vanta, Drata, or Secureframe, Fencer's findings sync back to your GRC platform automatically, so your evidence stays current without manual exports.
Take Fencer for a spin

Start scoping your pen test in minutes, or see a sample report first.