AI penetration testing

A full pen test on demand, in hours

See what an attacker could reach in your app, then close it fast. Fencer runs a full AI penetration test on demand, proves each finding with a working exploit, and fixes it with AI.

PDF
northwindlabs.dev Fencer Agent Penetration Test
Scoping
Penetration test lifecycle.
Scoping
9:14 AM
Scheduled
9:14 AM
In progress
9:31 AM
Ready for remediation
1:42 PM
Completed
2:47 PM
Details
9
Test configuration
Vulnerabilities
0
Waiting to start
Attack chains
0
Confirmed paths
Artifacts
0
Evidence
Severity
Title
Status
3 selected Linear
Vulnerability Details
Mass assignment allows self-registration as an admin user
VULN-1BA6
 Critical Confirmed
PROOF OF CONCEPT
POST /api/v1/users/ {"email":"attacker@example.com","role":"admin"} → HTTP 201 role:admin present in created user object
REPRODUCTION STEPS
1.POST /api/v1/users/ with "role":"admin" in the request body alongside a valid email and password
2.Server responds HTTP 201; the created user object echoes role:admin, confirming the field was mass-assigned
3.Authenticate as the new user via POST /api/v1/auth/token; the issued JWT carries "role":"admin"
4.Call GET /api/v1/admin/billing/ with the token; the admin-only endpoint returns HTTP 200
IMPACT
Any unauthenticated visitor can create an administrator account and take over the tenant. With admin access an attacker can read every tenant's billing records, manage users, issue API keys, and persist beyond remediation of this endpoint. Confirmed against staging with billing data for all four tenants returned.
ART-118 · response capture attached to the report
Linear
CreateLinkUnlink
Select a team
Pick a team first
Pick a team first
Pick a team first
Cancel
Create Issues
Pen test evidence synced to Vanta

The problem

Annual pen tests can’t keep up with AI-enabled teams

Traditional pen testing runs once or twice a year, costs five figures, and takes weeks to schedule and return a PDF. By the time it lands, you have shipped past much of what it covered. Teams now build and release with AI at a pace annual testing was never designed for, so most of the year goes unexamined.

An open door standing alone in a field.

The solution

Red team your application on demand

Every test follows the OWASP Top 10 and the Web Security Testing Guide, the same methodology a human pen tester would use.

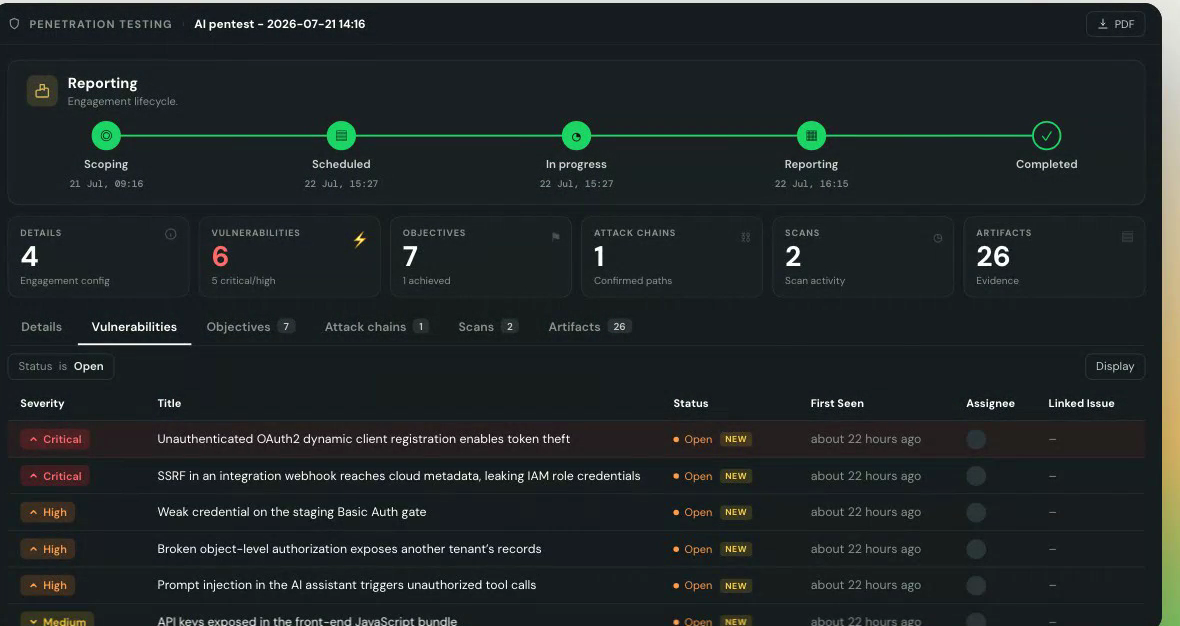
AI pen test UI

Built for the pace of AI-enabled development

Proof of exploit

Fencer shows the full attack path: the entry point, the steps, the data it reached, and the impact. A finding is marked high or critical only when an agent exploited it end to end.

Confirmed attack pathCritical · exploited
01Webhook accepts an attacker URL (SSRF)
02Reaches cloud metadata, leaks credentials

Compliance evidence

Every engagement produces a report and artifacts for SOC 2 and enterprise security questionnaires. Because you can run Fencer whenever you ship, that evidence stays current.

SOC 2 evidencePDF reportGRC sync

Free re-tests

Re-testing is unlimited, so you can confirm a finding is closed, ship the next change, and run it again.

Unlimited

re-tests to confirm a fix

No-charge guarantee

You only pay if our test finds a high or critical severity issue.

Free

if no high or critical issues are found

FAQ about Fencer AI penetration testing

What does it cost?

Fencer's pen test pricing is published: an autonomous AI-led test is $3,000, and a human-led test is $6,000. Continuous testing is custom-scoped, and platform plans include penetration test management. The AI-led test also comes with a guarantee: you only pay if it finds a high or critical severity issue.

Can it replace my annual pen test?

It gives you continuous coverage between the periodic human engagements auditors and customers expect, and Fencer offers a human-led test as well when you need one.

Does it satisfy SOC 2?

Every engagement produces a report and evidence artifacts for SOC 2 and enterprise questionnaires. Auditors still value a periodic human test for business logic, so many teams run Fencer continuously and keep their human test records in the same place.

How often can I run it?

On demand, as often as your product changes, rather than once or twice a year.

Can I buy only the penetration testing?

Yes. The pen test is a standalone offering (no platform plan required), and each finding still lands on the Fencer Security Platform so you can act on it.

Is this a real pen test or a scan?

It is a full penetration test. Fencer's agents chain weaknesses into a working attack path and prove the exploit with evidence, rather than listing weaknesses that might be exploitable.

Run your first test

Point Fencer at your app and see what an attacker could reach, with the fixes underway before you finish your coffee.