On-demand pen testing

Stop waiting for your next pen test

See what an attacker could actually reach. Fencer runs a full penetration test on demand, proves exploitable findings with working attacks, and retests fixes automatically.

Giveaway

Win a free pen test

Two TCP readers drawn every week through Nov 1.

You're entered!

Winners are drawn weekly. We'll email you if you win.

In partnership with The Cybersecurity Pulse

The problem

Your pen testing cadence shouldn't depend on someone else's calendar

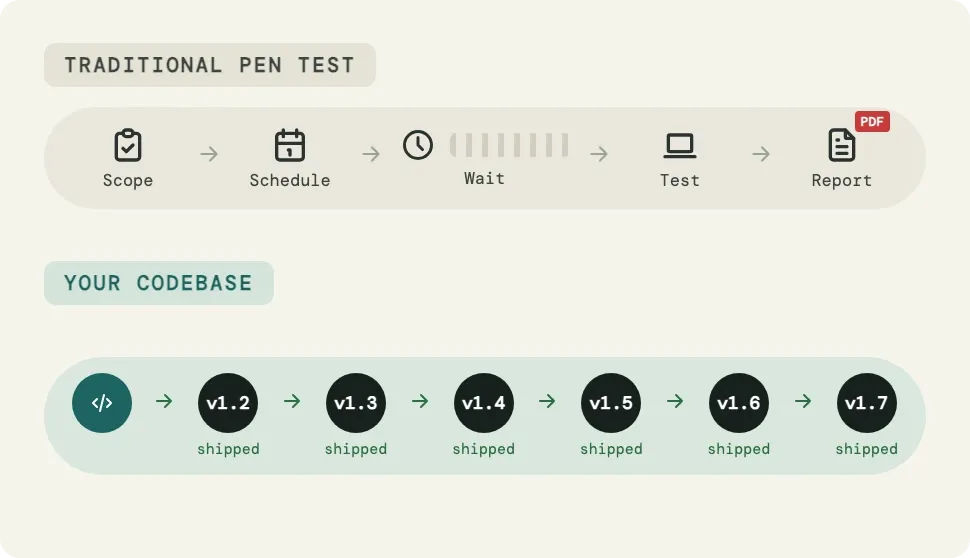
Traditional pen tests are built around someone else's schedule. You scope, you wait, you get a report, and by the time you close half the findings, enough code has shipped that the rest are already stale. The cadence was designed for software that moved slowly, and yours doesn't.

A traditional pen test moving from scope to schedule to a long wait to test to a PDF report, while the codebase below ships six versions over the same stretch.

The solution

Run a pentest. Fix what matters. Prove it's fixed.

You set the boundaries. Fencer does the testing, proves what it can exploit, and retests the fixes.

PDF
northwindlabs.dev Fencer Agent Penetration Test
Scoping
Penetration test lifecycle.
Scoping
9:14 AM
Scheduled
9:14 AM
In progress
9:31 AM
Ready for remediation
1:42 PM
Completed
2:47 PM
Details
9
Test configuration
Vulnerabilities
0
Waiting to start
Attack chains
0
Confirmed paths
Artifacts
0
Evidence
Severity
Title
Status
3 selectedLinear
Vulnerability Details
Mass assignment allows self-registration as an admin user
VULN-1BA6
 CriticalConfirmed
PROOF OF CONCEPT
POST /api/v1/users/ {"email":"attacker@example.com","role":"admin"}→ HTTP 201role:admin present in created user object
REPRODUCTION STEPS
1.POST /api/v1/users/ with "role":"admin" in the request body alongside a valid email and password
2.Server responds HTTP 201; the created user object echoes role:admin, confirming the field was mass-assigned
3.Authenticate as the new user via POST /api/v1/auth/token; the issued JWT carries "role":"admin"
4.Call GET /api/v1/admin/billing/ with the token; the admin-only endpoint returns HTTP 200
IMPACT
Any unauthenticated visitor can create an administrator account and take over the tenant. With admin access an attacker can read every tenant's billing records, manage users, issue API keys, and persist beyond remediation of this endpoint. Confirmed against staging with billing data for all four tenants returned.
ART-118 · response capture attached to the report
Linear
CreateLinkUnlink
Select a team
Pick a team first
Pick a team first
Pick a team first
Cancel
Create Issues
Pen test evidence synced to Vanta

01

Scope your test

Pick a verified domain, and Fencer maps the hosts and endpoints it finds. You confirm the exclusions and add test credentials for each user role.

02

Agents run and prove

Fencer maps the attack surface, tests for weaknesses, and chains them into attack paths. All findings are backed by a working exploit, not just a scanner alert.

03

Fix the findings

Every finding arrives with its attack path, the proof of exploit, and what the access reached. Send findings directly to Linear or Jira with the proof, severity, and owner already attached.

04

Fix and prove it today

Mark a finding fixed and Fencer retests it. No new engagement. No waiting for the pentester's calendar. Unlimited retests are included.

What you get

Built for the full pentest lifecycle

Full attack paths, proven end to end

Fencer shows what the attacker reached, what they couldn't reach, and where the attack stopped. Severity reflects demonstrated impact, not just theoretical exposure.

Automate the tedious half of a pen test

No parsing a PDF into tickets, no tracking down who owns what, no scheduling a retest to prove it closed. Findings arrive in Linear or Jira with severity, proof, and an owner, the retest runs when you mark one fixed, and the evidence syncs to Vanta, Drata, or Secureframe.

Stay covered between pen tests

Your attack surface changes after the engagement ends. Fencer continuously scans your network and domains so newly exposed hosts, vulnerabilities, and certificate issues don't have to wait until the next pentest. One year included.

Reports for your team, your auditor, and your customers

Every engagement produces a technical report with the detailed findings, an executive summary you can share with customers, auditors, and your security team, and a remediation report recording each finding through to resolved.

Pricing

A pen test, plus a year of scanning for just $3,000

Point solutions

Fencer

Annual pen test

$5–$15K/yr

Included

On-demand pen test, unlimited retests

Network vulnerability scanning

~$4K/yr

Included

Continuous network scanning

Domain monitoring

~$5K/yr

Included

Domain exposure monitoring

GRC evidence sync

Not included

Included

Evidence sync to Vanta, Drata, Secureframe

$14,000–$24,000

/ yr

Testimonials

Teams that replaced the scheduled engagement

Renew logo

Managing pentest findings used to eat up tons of our time. We'd parse reports, manually file tickets, build trackers, and then coordinate the retest. With Fencer, findings go straight into Linear with everything our team needs to act on them. Remediation becomes part of the normal sprint instead of a project on top of it.

Justin Rhoades

Justin Rhoades

CTO, Renew

RTOPilot logo

A customer asked for pen test evidence. We ran Fencer's AI pen test, got findings with accurate severity and clear remediation steps, and handed them the report. It replaced what would have been a full third-party engagement.

Manning Blackall

Manning Blackall

CEO, RTOPilot

Fontana logo

Fencer's AI pen testing delivered precise and easy-to-understand results that I was able to action immediately. As a solo founder, the service was invaluable and exactly what I needed from a security tool.

Gabriel Garayalde

Gabriel Garayalde

Founder, Fontana

Stop scheduling pen tests around someone else's calendar

Two Cybersecurity Pulse readers start one free every week through Nov 1.